Secure Custom Software Development
We design security into your architecture from the first sprint, so your product is ready for HIPAA, SOC 2 and GDPR before the first enterprise deal.
 100% audit readiness
 6 compliance frameworks
 BAA · DPA · SLA signed

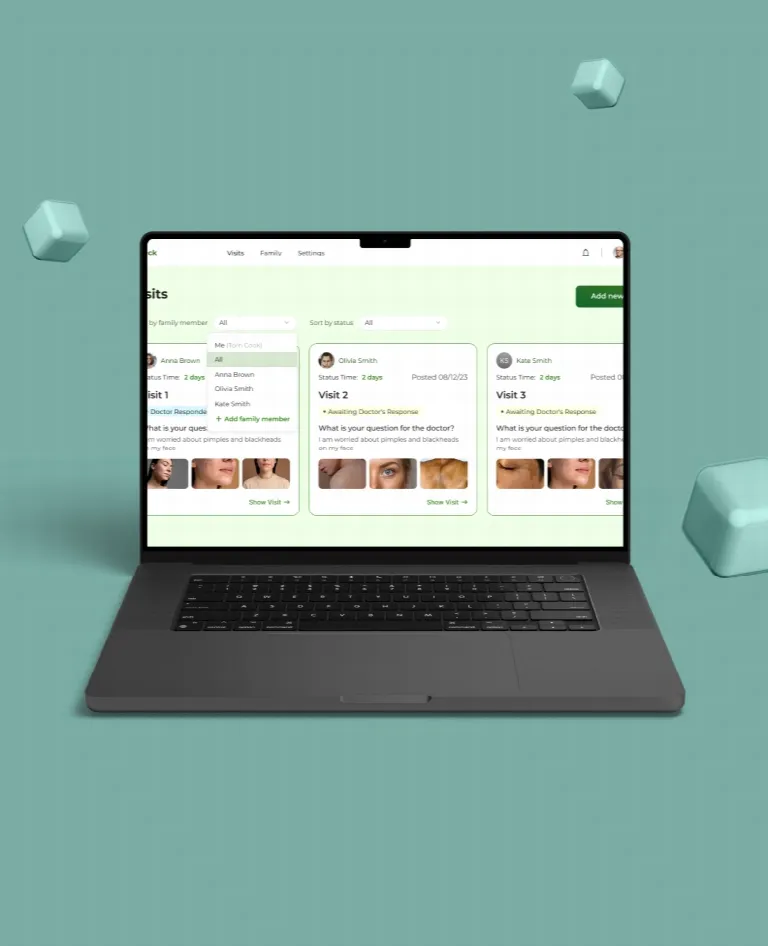
AI-powered dermatology platform for a healthcare company
““Corpsoft Solutions has been exceptional in their delivery,” says Jon Friedman, co-founder and CEO of DermSnap LLC”
“Corpsoft Solutions has delivered a functional platform with seamless UX and robust infrastructure, which has received positive user feedback. The team has a structured approach, communicates effectively, and is timely, responsive, and committed. The team's professionalism and expertise stand out.”
Most regulated products aren't built for compliance. They're rebuilt for it — at the worst possible moment.
Generic dev shops ship working software. Security frameworks get delivered. Neither produces secure application development that holds up under an enterprise security review, a HIPAA audit, or EU AI Act classification — without significant architectural rework at exactly the moment your deal pipeline, fundraise, or regulatory deadline can least afford it.
Compliance planned for later
You’re building a healthcare platform, AI product, or enterprise SaaS, and you plan to meet HIPAA-compliant software development standards before your first enterprise deal or audit. By the time that moment arrives, your architecture is set, vendors are integrated, and a retrofit costs multiples of what security in software development from day one would have.
No secure SDLC on the team
The team shipping your product is functional — but no one follows a secure SDLC, reviews vendor contracts for BAA and DPA coverage, or validates that your cloud configuration and APIs are eligible for regulated environments.
AI features without governance
You're integrating AI features into a product that processes patient data, financial records, or EU user data — without audit logging, model governance, or decision traceability that GDPR Article 22 and EU AI Act require before you can close an enterprise deal or enter a regulated market.
Architecture set before compliance
Most teams working on regulated software think compliance can wait until the architecture is set. It can't — because by then, vendor integrations, data flows, and access controls are already baked in.
Security designed in from the first sprint
Encryption, access control, audit logging and data segmentation become architectural decisions in your product from day one. Tell us what you’re building, and we’ll show where security belongs in it.

What you have when the build is complete
Compliance-Native Architecture
Your product is designed against the frameworks that apply to it: HIPAA, SOC 2, ISO 27001, GDPR, EU AI Act and NIS2. Access management, encryption, data flows and vendor integrations meet audit requirements from the first release.
Secure Data Architecture & AI Governance
Encryption at rest and in transit, data segmentation and monitoring, with input and output paths designed to stay compliant as your product scales. For AI products: model lineage, decision logging, EU AI Act classification documentation and GDPR Article 22 safeguards built into the pipeline.
Audit Trail, Evidence & Documentation
Logs, implementation records and compliance evidence are generated throughout the development lifecycle, ready for SOC 2 Type II, ISO 27001 or HIPAA review from the first day in production. Your compliance documentation is written by the engineers who built your system.
BAA & Vendor Coverage
A BAA is signed with every client before the engagement begins. Every third-party integration is reviewed and documented for regulatory coverage.
Enterprise-Ready Security Posture
Your product is ready for enterprise security questionnaires, SOC 2 audits and procurement reviews in regulated industries, with no emergency architecture work when the first major deal appears.
What standards do we build to
Corpsoft Solutions builds regulated software to the secure software development best practices that auditors, enterprise procurement teams, and regulators actually enforce. Not a proprietary checklist — a structured implementation of recognized external benchmarks, embedded into architecture from the first sprint.
NIST Cybersecurity Framework 2.0
The primary structure for designing, implementing, and validating security controls across your architecture. We use the Govern → Identify → Protect → Detect → Respond → Recover sequence to map control coverage into your system from the first sprint.
NIST AI Risk Management Framework (AI RMF)
For products with AI or ML components: model governance, risk tiering, explainability, and traceability built into the pipeline against NIST’s Govern, Map, Measure, Manage structure. It also supports the documentation EU AI Act requires for high-risk systems.
OWASP API Security Top 10
API authentication mechanisms, authorization controls, data exposure boundaries, and object-level access — designed and implemented against OWASP’s current top-10 classification. Applied during architecture design and enforced throughout the development lifecycle.
ISO 27001 Annex A
Information security control domains — access control, cryptography, operations security, supplier relationships — implemented as architectural decisions from the start. The output is structured and ready for ISO 27001 certification review.
SOC 2 Trust Service Criteria
Security, availability, and confidentiality criteria built into the system from day one — access controls, audit logging, availability monitoring — so evidence exists from the day your product goes into production.
EU AI Act — Risk Classification
High-risk AI system requirements — transparency obligations, human oversight mechanisms, technical documentation, incident reporting — implemented for products operating in EU markets or processing EU user data. Designed in before the system goes to production.
HIPAA Security Rule §164.312
Technical safeguard requirements for access control, audit controls, integrity, and transmission security — implemented at the architecture level for all products handling protected health information, well before the first hospital conversation.
GDPR Article 32
Technical and organizational measures for data security — encryption, pseudonymization, confidentiality, and integrity — are designed into data flows and vendor configurations from the first sprint.
Principle of Least Privilege
IAM roles, permission scopes, and access paths designed around minimum-required access from the start. Excess access is one of the most common sources of enterprise security failures and audit blockers.
Vendor DPA / BAA Coverage
Every third-party integration reviewed against contractual compliance requirements before it's added to the stack: which vendors need Data Processing Agreements under GDPR, which need Business Associate Agreements under HIPAA, and which need to be replaced with compliant alternatives.
What working with Corpsoft Solutions looks like in numbers
100% audit readiness
Every product we build is ready for HIPAA, SOC 2 Type II or ISO 27001 review from the first day in production. Logs, evidence and documentation are in place before the auditor asks for them.
Outputs:
Case study: Comprehensive Remote Patient Monitoring Platform for Chronic Care Management
Learn more
5.0 rating on Clutch
Across 20+ verified client reviews in healthcare, AI and enterprise SaaS, with consistent scores for quality, schedule and willingness to refer.
6 compliance frameworks
HIPAA, SOC 2 Type II, ISO 27001, GDPR, EU AI Act and NIS2, built natively into your product’s architecture from day one.
Outputs:
Case study: A Revolutionizing Platform For Pediatric with AI-Powered Workflow Optimization
Learn more10,000+ users
Users on a vision screening platform we built with compliance designed in from the first sprint. In production since 2020 with no compliance incidents.
What we see in software built without compliance-native architecture
Shared production-wide admin access
Admin roles with production-wide access shared across the engineering team — one compromised account or a departing engineer creates a direct path to every database, storage bucket, and configuration file in the system.
PHI and PII in logs and analytics
PHI and PII are stored in application logs or piped into third-party analytics tools — a HIPAA and GDPR violation that exists before the product reaches its first regulated customer.
AI pipelines without traceability
AI inference pipelines logging model outputs but not inputs, model versions, or decision context — fails EU AI Act traceability requirements and GDPR Article 22 automated decision-making obligations before the first EU market conversation.
APIs returning full data objects
APIs returning full data objects instead of only what the request requires — excessive object-level exposure that fails OWASP API Security Top 10 and appears in every enterprise security questionnaire.
Integrations without DPA or BAA
Third-party integrations — analytics platforms, communication tools, payment processors — added to the stack without DPA or BAA coverage, creating undocumented compliance liability that no one discovers until an audit or enterprise procurement review.
Secure development services
An end-to-end engagement, or standalone capabilities for teams that need a targeted security layer without a full build.
Service 1
DevSecOps Services
Security integrated into every stage of your CI/CD pipeline — automated checks, policy enforcement, and vulnerability detection built into the development workflow before code reaches production.
Learn more
Service 2
Vulnerability Management
Continuous scanning, risk prioritization, and remediation from $200/month. AI-powered detection finds the issues, and our engineers fix them.
Learn more
Service 3
Software Security Testing
SAST, DAST, and manual security review across your codebase and APIs, mapped to OWASP Top 10 and your target compliance framework.
Learn more
Build it right before an audit makes you rebuild
A 30-minute technical call with a Corpsoft Solutions engineer, no commitment. We’ll identify the frameworks that apply to your product and map what secure development looks like for it before the first sprint.
How We Build
Every engagement follows a secure software development framework built on one principle: compliance controls are architectural decisions, not remediation tasks.
- 01
Regulatory Mapping
Step 1
We start with a software security assessment of your regulatory environment — identifying which frameworks apply to your product, market, and user data: HIPAA, SOC 2 Type II, ISO 27001, GDPR, EU AI Act, NIS2, or a combination. Architecture decisions don't begin until the compliance requirements are mapped.
- 02
Controls-by-Design
Step 2
Security controls are embedded before the first sprint. IAM roles are designed around least-privilege, encryption configuration, vendor selection reviewed for DPA and BAA eligibility, and threat modeling against your specific risk profile. The result: a system that doesn’t need to be rebuilt before your first enterprise deal.
- 03
Secure Development Lifecycle
Step 3
Every sprint follows a secure software development process — OWASP-aligned coding practices, security testing throughout development, code review against compliance controls. Security is not a final check before launch. It runs in parallel with every feature build.
- 04
Data Flow Architecture & AI Governance
Step 4
Data inputs, outputs, and storage paths designed for compliance from day one. For products with AI: model governance, audit logging, decision traceability, and EU AI Act risk classification built into the pipeline — not added after a regulatory review flags the gaps.
- 05
Audit Artifact Generation
Step 5
Evidence, documentation, and audit trails generated throughout development — not assembled before a certification review. Access logs, control implementation evidence, and change records — ready for SOC 2 Type II, ISO 27001, or HIPAA audit from day one of production.
Why regulated teams choose Corpsoft Solutions
Security consultants deliver findings. Generic dev shops deliver code. Neither takes responsibility for the system behaving correctly under audit or enterprise security review.
Corpsoft Solutions engineers compliance into architecture and takes contractual liability — BAA, DPA, SLA signed before work begins. If the system fails an audit tied to our architecture decisions, we fix it.
Trusted by growing companies, past the MVP stage
 |20+ reviews
5★/21
Check out what they have to say about working with us.
"Corpsoft Solutions has been exceptional in their delivery."
Corpsoft Solutions has delivered a functional platform with seamless UX and robust infrastructure, which has received positive user feedback. The team has a structured approach, communicates effectively, and is timely, responsive, and committed. The team's professionalism and expertise stand out.
“We could mention their technical expertise and wonderful work, but communication is their most impressive trait.”
The client has saved $200,000 and gained an incalculable amount of new business thanks to the platform’s efficiency and professional look. Corpsoft.io has delivered outstanding work, but they’ve excelled overall in project management. They use SCRUM sprints and Jira and are responsive partners.
 |20+ reviews
5★/21
Check out what they have to say about working with us.
"Corpsoft Solutions has been exceptional in their delivery."
Corpsoft Solutions has delivered a functional platform with seamless UX and robust infrastructure, which has received positive user feedback. The team has a structured approach, communicates effectively, and is timely, responsive, and committed. The team's professionalism and expertise stand out.
“We could mention their technical expertise and wonderful work, but communication is their most impressive trait.”
The client has saved $200,000 and gained an incalculable amount of new business thanks to the platform’s efficiency and professional look. Corpsoft.io has delivered outstanding work, but they’ve excelled overall in project management. They use SCRUM sprints and Jira and are responsive partners.
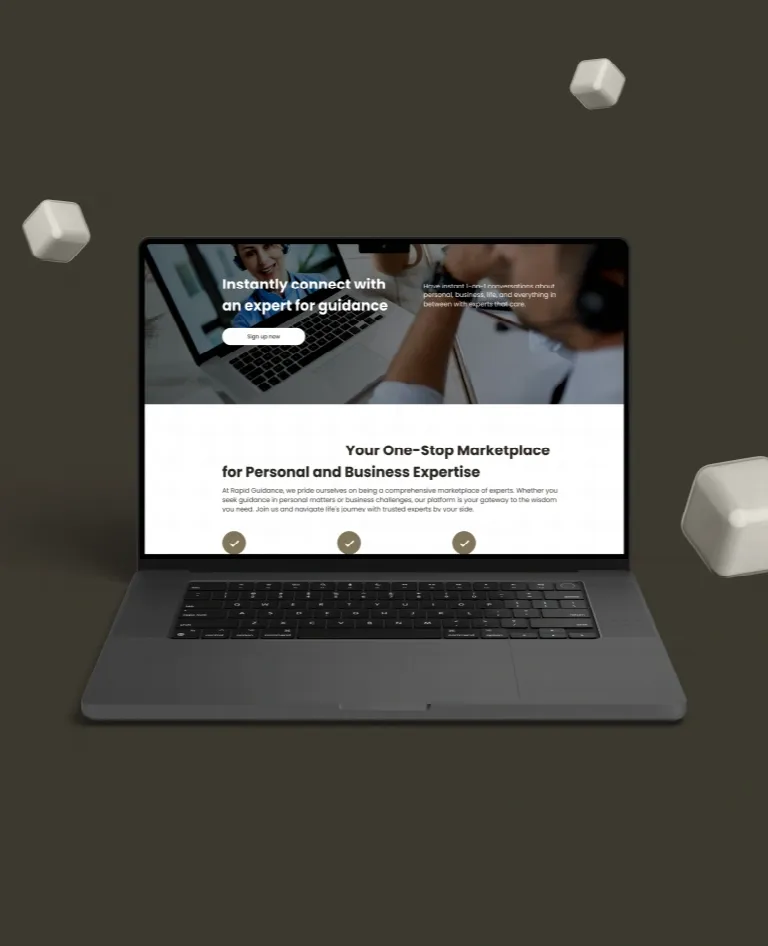
See the architecture in production
Consulting marketplace reached 10,000+ users and 5,000+ consultations in 3 months
Complicated booking with unclear availability
Secure video calls inside the platform
Experts managing profiles and schedules by hand
Scaling to more users and mobile access
Real-time availability and one-click slot booking
Encrypted WebRTC video calls for booked sessions
Expert dashboard for profiles and live availability
Scalable architecture and PWA for mobile access
- 10,000+ registered users in the first 3 months
- 5,000+ consultations completed with a 4.9/5 average rating
- 80% expert booking rate within the first month
AI-powered dermatology platform built to handle sensitive patient data securely
Handling sensitive patient images without data leakage
Ensuring HIPAA-compliant AI diagnostics
Fragmented dermatology workflows across tools
Slow diagnosis and long patient wait times
Secure image processing with encryption and audit trails
HIPAA-aligned architecture with governed AI models
Unified platform for end-to-end dermatology workflows
AI-assisted diagnostics to accelerate doctor decisions
- Secure, compliant AI diagnostics (HIPAA-aligned)
- End-to-end dermatology workflow in one platform
- 1.5x faster diagnosis & 1–2 minute review time
- Up to 4x reduction in patient wait times
Build audit-ready software from the first sprint
Tell Andrii about your product, your regulatory environment and your timeline. In a 30-minute call, he’ll outline what a compliance-native build looks like for you across HIPAA, SOC 2 Type II, ISO 27001, GDPR or the EU AI Act.
Book a Discovery Call with AndriiBuild audit-ready software from the first sprint
Tell Andrii about your product, your regulatory environment and your timeline. In a 30-minute call, he’ll outline what a compliance-native build looks like for you across HIPAA, SOC 2 Type II, ISO 27001, GDPR or the EU AI Act.
Book a Discovery Call with Andrii
Andrii Svyrydov
Founder & CEO of Corpsoft Solutions · ex-Head of Tech at a software company with 1,500+ delivered projects
Build software that passes audits, closes enterprise deals, and enters regulated markets — without a rebuild.
Security consultants deliver findings. Generic dev shops deliver code. Neither takes responsibility for the system behaving correctly under audit or enterprise security review. Corpsoft Solutions engineers compliance into architecture and takes contractual liability — BAA, DPA, SLA signed before work begins. If the system fails an audit tied to our architecture decisions, we fix it.
No, and this is a structural decision, not a promise. We run a compliance track in parallel with your product track. Controls, documentation, and audit evidence are generated throughout development — not in a sprint before launch. Your engineering team builds features. The compliance layer runs alongside, not in place of it.
We design systems to adapt. The secure software development best practices we follow from day one — modular access control design, documented data flows, audit-ready logging — mean that when requirements evolve (EU AI Act enforcement updates, NIS2 amendments, GDPR guidance changes), the system adapts without a full rebuild.
Earlier than most teams think. The investment in building compliance into architecture from day one is a fraction of the cost of retrofitting it when an enterprise deal, investor due diligence, or hospital procurement review makes it unavoidable. The teams that delay compliance are the ones who rebuild — at the exact moment growth is accelerating.
HIPAA, SOC 2 Type II, ISO 27001, GDPR, EU AI Act, NIS2 — and combinations. Most regulated products need more than one framework simultaneously. We map your regulatory requirements at the start of every engagement and build to all applicable frameworks in a single development track.
Both. For new products, we design compliance-native architecture from the first sprint. For existing systems with compliance debt, we start with a 7-Day Risk Assessment of your current architecture, data flows, and vendor integrations — and build a remediation path. The approach differs; the outcome is the same.
Yes. We sign a mutual NDA and Data Processing Agreement before any access is granted. For healthcare products handling protected health information, we sign a Business Associate Agreement. For enterprise engagements requiring additional contractual coverage, we accommodate before work begins.
Ready to discuss your project with us?Not sure where to start?
Drop us a line about your project or challenge — we'll take it from there.
 Typical response time1 hour on business days