Vulnerability Management as a Service
Most scanners stop at a list of findings. Our engineers fix every issue they find, while your product gets AI-powered continuous scanning across cloud, containers and applications, prioritized by real risk.
 AI-powered continuous scanning
 Risk-based prioritization
 From $200/month
 6 compliance frameworks

Most vulnerability scanners generate reports. Not fixes.
A scan finds hundreds of issues, and most vulnerability management tools stop right there. You get a dashboard full of severity scores, no sense of which ones an attacker could actually reach, and no one on the hook to close them. The list grows every week faster than anyone can work through it.
No idea which findings matter
We have 400 open findings and no idea which ten actually matter.
A PDF, and nothing fixed
Our last vendor just handed us a PDF. Nothing got fixed.
A backlog that only grows
Every scan adds to the backlog faster than we can close it.
Security fixes eat the roadmap
Every sprint, security fixes push our roadmap back again.
What vulnerability management as a service actually includes
Vulnerability management as a service means continuous, AI-powered scanning across your cloud infrastructure, containers, and applications — not a quarterly report. We prioritize findings by actual exploitability and business impact, not raw CVSS score, and the same engineers who run the scan close the highest-risk gaps directly. AI-powered continuous scanning + remediation. From €200/month, across three tiers scoped to how much of your environment needs coverage.
AI-Powered Scanning
Risk-Based Prioritization
Continuous Monitoring
Engineering-Led Remediation
Three terms people mix up — and what each one actually means
These three get used interchangeably, and they're not the same thing. Knowing the difference matters for scoping what you're actually buying.
Vulnerability Management
Finding, prioritizing, and fixing security weaknesses across your systems on an ongoing basis.
Not the actual installation of patches — that's usually your internal IT/ops function, coordinated with our prioritized list.
Patch Management
Applying vendor-released fixes to known software vulnerabilities on a schedule.
Not risk-aware on its own — it patches what's available, not necessarily what's most exploitable first.
Exposure Management
A broader, continuous view of your entire attack surface — assets, misconfigurations, identities, not just CVEs.
Not a replacement for vulnerability management — it's the wider lens vulnerability management sits inside.
Vulnerability Management
Finding, prioritizing, and fixing security weaknesses across your systems on an ongoing basis.
Not the actual installation of patches — that's usually your internal IT/ops function, coordinated with our prioritized list.
Patch Management
Applying vendor-released fixes to known software vulnerabilities on a schedule.
Not risk-aware on its own — it patches what's available, not necessarily what's most exploitable first.
Exposure Management
A broader, continuous view of your entire attack surface — assets, misconfigurations, identities, not just CVEs.
Not a replacement for vulnerability management — it's the wider lens vulnerability management sits inside.
What's covered
Risk-Based Scanning
Continuous, AI-powered scanning across your environment, with findings ranked by exploitability and business impact, so your team sees what can actually hurt the product first.
Timeline & Output:
Continuous
Cloud & Multi-Cloud Coverage
Scanning built for cloud-native environments, including AWS. As an AWS Select Tier Services Partner, we map coverage to your actual cloud setup and account structure.
Timeline & Output:
Continuous
Container & Application Scanning
Running containers and deployed applications are scanned continuously after release, which complements the build-time checks embedded in your pipeline.
Timeline & Output:
Continuous
Remediation & Reporting
Findings get fixed in order of risk by the same engineering team that found them, with an audit-ready evidence trail for your next compliance review or security questionnaire.
Timeline & Output:
As findings close
What working with Corpsoft Solutions looks like in numbers
100%
Audit readiness
Every finding we fix is documented with evidence, so your product stays ready for HIPAA, SOC 2 Type II or ISO 27001 review.
Related case study:
Comprehensive Remote Patient Monitoring Platform for Chronic Care Management
5.0
Rating on Clutch
Across 20+ verified client reviews in healthcare, AI and enterprise SaaS.
Related case study:
Clutch profile6
Core regulations and standards
HIPAA, SOC 2 Type II, ISO 27001, GDPR, EU AI Act and NIS2. Every finding is prioritized against the frameworks your product needs.
Related case study:
Telemedicine Platform for Vision Screening and Testing7 days
Free risk assessment
A prioritized map of the vulnerabilities in your cloud, containers and applications, with what to fix first.
Related case study:
Read more about this Risk Assessment of yoursKnow exactly which vulnerabilities actually put you at risk.
A short scoping call maps what's running in your environment, what a risk-based scan would surface, and which of the three tiers actually fits.

How vulnerability management as a service works
- 01
Discovery & Asset Mapping
Step 1
We map what's actually running across your cloud, containers, and applications — you can't scan, let alone prioritize, what you don't know you have.
- 02
Risk-Based Scanning
Step 2
AI-powered continuous scanning runs across the mapped environment, surfacing findings ranked by real exploitability and business impact, not raw severity score alone.
- 03
Prioritized Remediation
Step 3
The highest-risk findings get fixed directly by our engineers, in parallel with your roadmap, not queued behind a separate ticket system.
- 04
Continuous Monitoring
Step 4
Scanning keeps running as your environment changes, so new exposure gets caught the week it appears, not at the next quarterly review.
- 05
Maturity Review
Step 5
Periodically, we benchmark your program against a vulnerability management maturity model, so you can see the trend, not just the current snapshot.
What you have once vulnerability management is actually running
Every deliverable is something you can hand to an auditor, a security reviewer, or your own engineering team — not a PDF that sits in a folder.
Risk-Prioritized Vulnerability Backlog
Findings ranked by exploitability and business impact, not a flat severity list nobody can act on.
Continuous Scan Coverage
Cloud, containers, and applications scanned on an ongoing basis, catching new exposure as your environment changes.
Audit-Ready Evidence Trail
Scan history and remediation records generated from day one, ready for your next audit or security questionnaire.
Framework-Mapped Reporting
Findings and fixes tracked against the standards your compliance program actually requires, not a generic export.
Vulnerability Management Maturity Baseline
A documented starting point, benchmarked and re-measured over time, so leadership sees a trend, not a one-off score.
Engineering, Not Just a Report
The same team that finds the gap closes it, so remediation doesn't become a second vendor search.
Stop drowning in findings. Start closing the ones that matter.
Tell Andrii what’s running in your environment. He’ll map what a risk-based scan would find and which plan fits your product.
Book a call with AndriiStop drowning in findings. Start closing the ones that matter.
Tell Andrii what’s running in your environment. He’ll map what a risk-based scan would find and which plan fits your product.
Book a call with Andrii
Andrii Svyrydov
Founder & CEO of Corpsoft Solutions · ex-Head of Tech at a software company with 1,500+ delivered projects
Trusted by growing companies, past the MVP stage
 |20+ reviews
5★/21
Check out what they have to say about working with us.
"Corpsoft.io team delivers quickly."
Corpsoft.io has successfully delivered the custom product using 7.5 sprints, meeting the client's business goals. The team delivers quickly and provides daily updates and weekly video conferences. They ask tough questions and respond to every single comment or question.
|20+ reviews5★/21
Check out what they have to say about working with us.
"Corpsoft.io team delivers quickly."
Corpsoft.io has successfully delivered the custom product using 7.5 sprints, meeting the client's business goals. The team delivers quickly and provides daily updates and weekly video conferences. They ask tough questions and respond to every single comment or question.
See vulnerability management in production
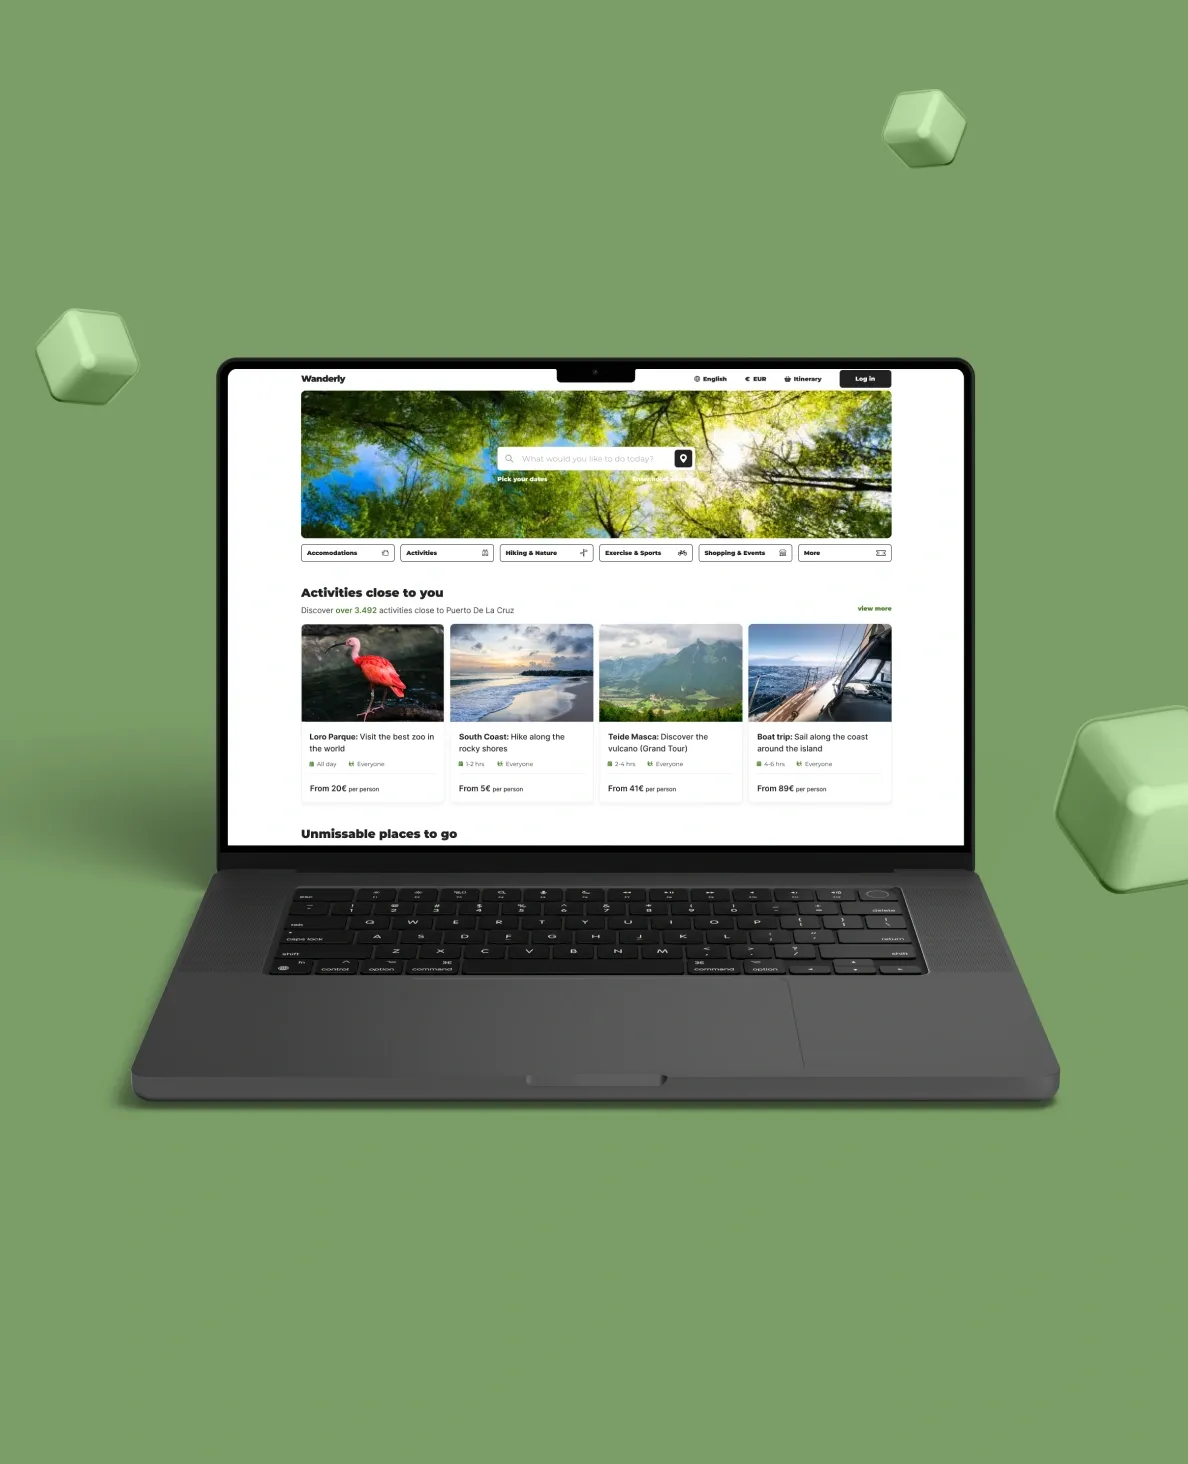
Travel booking platform raised booking conversion 30% with a live activity map
Activities scattered across several booking sites
Hard to find nearby events in real time
Syncing hotel data and third-party activities
Protecting traveler and payment data under GDPR
Single catalog with filters for location and availability
Interactive map with live events and route building
API integrations with hotel databases and aggregators
Encryption and access controls aligned with GDPR
- 30% higher booking conversion with map-based search
- First release live in 3 months
- Scalable architecture ready for new cities and languages
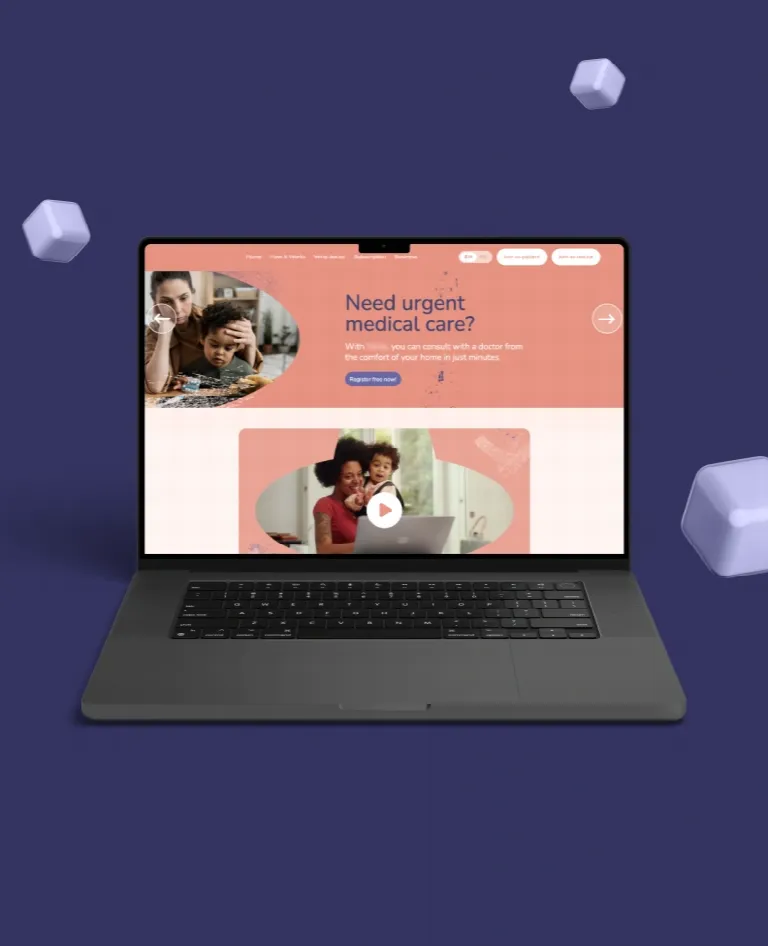
A Scalable Platform for Seamless Telehealth Services and Remote Patient Care
Secure video consultations with access to medical data
Slow remote diagnosis and treatment planning
Growing patient volume across regions
Encrypted video visits with RBAC and audit logging
AI recommendation engine with doctor review of outputs
Modular Laravel backend for scaling and integrations
- 3x more patients reached across regions
- 40% faster treatment planning with AI recommendations
- HIPAA-aligned video consultations and medical data management
Further reading on this topic
 March 13, 202624 min read
AI Governance in Practice: How to Manage Risk, Compliance, and Accountability at Enterprise Scale
Discover how to operationalize AI governance and build AI governance frameworks to manage risk and accountability.
View more
 February 5, 202620 min read
Assessing Healthcare Regulatory Compliance and Risk in Legacy Software Systems
Legacy healthcare software accumulates compliance risks as regulations evolve beyond system capabilities. Assessment reveals modernization needs.
View more September 4, 202613 min read
Enterprise AI Security: What Buyers Actually Ask Before They Sign
Your SOC 2 report covers most of the vendor questionnaire, but not its AI section. What enterprise buyers ask about your model, data path and retention, and which artifacts close the review.
View more


Questions clients ask before we start
Vulnerability management finds, prioritizes, and fixes security weaknesses on an ongoing basis. Patch management is narrower — applying vendor-released fixes on a schedule, without necessarily accounting for which ones are most exploitable first. We coordinate a prioritized fix list; the actual patch deployment is typically your internal IT or ops function, working from that list.
AI-powered continuous scanning across your cloud, containers, and applications, risk-based prioritization instead of a raw severity list, and remediation by the same engineers who ran the scan — not just a findings report. Pricing starts at €200/month across three tiers, scoped to how much of your environment needs coverage; the right tier depends on your setup, which we scope on a call.
Yes, Corpsoft Solutions is an AWS Partner, Select Tier Services, with AWS Certified Solutions Architects on the team, so scanning is built against your actual cloud environment and its existing tooling, not a cloud-agnostic template. Multi-cloud setups are covered the same way, mapped to each environment individually.
We benchmark your program against a vulnerability management maturity model at the start, then re-measure periodically so you can see the trend, not just a single snapshot. Beyond the maturity score, the metrics that matter most are time-to-remediation on high-risk findings and how much of your actual environment is under continuous coverage.
No, exposure management is the broader, continuous view of your entire attack surface: assets, misconfigurations, identities, and more, not just known CVEs. Vulnerability management is the core of that picture, focused specifically on finding and fixing software vulnerabilities. Most companies need the vulnerability management piece solid before exposure management adds real value on top.
Vulnerability management is continuous scanning and remediation of your already-deployed infrastructure. DevSecOps Services builds checks directly into your CI/CD pipeline, catching issues before code reaches production. Software Security Testing is a separate, dedicated engagement for SAST, DAST, and manual security review. The three work well together, but each answers a different question.
Standard scanning ranks findings by raw severity score alone, which buries the handful that actually matter under hundreds that don't. Risk-based vulnerability management ranks findings by real exploitability and business impact instead — what an attacker could actually reach, and what it would cost you if they did — so the highest-risk items get fixed first.
Pricing starts at $200/month, across three tiers scoped to the size of your environment and how much coverage and remediation support you need. The exact fit depends on your setup — a short scoping call gives you a real number instead of a generic monthly figure that doesn't reflect what you're actually running.
Ready to discuss your project with us?Not sure where to start?
Drop us a line about your project or challenge — we'll take it from there.
 Typical response time1 hour on business days