Know exactly where your compliance gaps are. In 7 days
 Starts within 48 hours
 Read-only access — nothing is changed
 100% audit readiness
We connect to your environment with read-only access and review your AWS or GCP architecture and cloud security compliance controls, IAM roles, API authentication flows, encryption configuration, vendor access paths, and AI inference pipelines — then return a prioritized report: Critical, High, Medium, Low — with effort estimates per finding. No sales pitch. Just findings.
"The team is very professional and pleasant to work with, and their attentiveness is very noticeable and present."


"Corpsoft.io consistently updates their task list, prepares for sprints, and checks and marks the feedback document daily. Moreover, the team manages the project well without micromanagement, proactively informs the client about the project's status, and promptly addresses all their requests."
Anonymous
Executive, Reportil
Most compliance projects start too late — when the deal is already at risk
Consultants deliver frameworks. Auditors find gaps after the fact. Neither gives you a clear picture of where the audit blockers are before an enterprise deal stalls in security review, a SOC 2 audit comes back with findings, or a hospital procurement team asks questions you can't answer.
Your enterprise deal is stuck in security review — and you don't know which specific control failures are blocking it.
You're preparing for SOC 2 readiness, ISO 27001 gap analysis, or HIPAA certification with no clear picture of what actually needs to change in your codebase and infrastructure.
You're shipping AI features without knowing whether your data flows, model governance, or decision logging meet GDPR Article 22 or EU AI Act requirements.
What the 7-Day Risk Assessment covers
A software compliance audit that goes beyond documentation — a technical deep-dive into your architecture, data flows, access controls, and third-party integrations — mapped against the compliance requirements that apply to your specific product and market.
We look at where your systems actually are, not where your documentation says they are. The output isn't a policy template. It's a specific, prioritized list of what's broken, what it costs to fix, and what to address first.

AWS / GCP Architecture Review

IAM Security Audit & Control

Encryption at Rest & in Transit

API Authentication Mechanisms

Vendor Risk Assessment

AI/ML Governance Gaps

Prioritized Remediation Roadmap
What we find in 80% of assessments

Overprivileged IAM roles with no least-privilege enforcement — one compromised account reaches everything

Missing or incorrectly scoped vendor DPAs and BAAs — third-party integrations creating undocumented compliance liability

Broken audit logs — records exist, but can't be used as evidence in a SOC 2 or OCR review

No AI decision traceability — model outputs logged, but inputs and model versions aren't — fails EU AI Act and GDPR Article 22

API tokens with no rotation policy or expiration — some active since the product was first built
What working with Corpsoft Solutions looks like in numbers
100%
Audit readiness
Across all of Corpsoft Solutions' compliance engagements. Every client passes certification — HIPAA, SOC 2, ISO 27001. If a finding in our report contributes to a failed audit, we fix it at no additional cost.
5.0
Rating on Clutch
Across 20+ verified client reviews — consistent across quality, schedule, cost, and willingness to refer.
Related case study:
Our Clutch profile
10+
Years delivering software in regulated industries
Healthcare, AI, enterprise SaaS. Every assessment is run by engineers who have shipped and audited production systems, not consultants who review documentation.
Related case study:
Complex business tool development for the 3D model construction10,000+
Users in production
On a Corpsoft-built telemedicine platform for vision screening — running in production since 2020 with no compliance incidents.
Not sure if you have compliance exposure? That's exactly the point.
Most software companies discover their biggest audit blockers during a certification review — not before it. The 7-Day Risk Assessment gives you the full picture first: every control failure, every vendor gap identified through a structured compliance gap analysis, every AI governance blind spot — ranked by severity and mapped to a remediation path. Before a deal stalls. Before an auditor finds it.
Start my free assessmentNot sure if you have compliance exposure? That's exactly the point.
Most software companies discover their biggest audit blockers during a certification review — not before it. The 7-Day Risk Assessment gives you the full picture first: every control failure, every vendor gap identified through a structured compliance gap analysis, every AI governance blind spot — ranked by severity and mapped to a remediation path. Before a deal stalls. Before an auditor finds it.
Start my free assessment
Andrey Svyrydov
Founder / CEO / Solution Architect
How the 7-Day Risk Assessment works
- 01
Scoping call
We align on your regulatory profile, target frameworks — SOC 2, HIPAA, ISO 27001, GDPR, EU AI Act — and the systems in scope. No access required at this stage. Takes 30 minutes.
- 02
Environment access
Days 1-2
Read-only connection to your cloud infrastructure and security compliance, repositories, data flow documentation, and third-party integrations.
- 03
Automated scan & analysis
Days 3-5
Automated scanning of your cloud configuration, IAM policies, and dependency graph, paired with manual review of the highest-risk findings — the core analysis work behind the report.
- 04
Findings report
Days 6-7
Prioritized risk triage, effort estimates per finding, and remediation paths. Delivered before the debrief call for early review.
- 05
Debrief session
Days 6-7
A live walkthrough of findings with the assessing engineer. We answer technical questions, clarify remediation options, and outline full implementation steps.
The regulations and standards behind the assessment
The 7-Day Risk Assessment maps your architecture against recognized benchmarks that auditors, enterprise procurement, and regulators actually use. Not a proprietary checklist—a structured review against external standards.

NIST Cybersecurity Framework 2.0
The blueprint for identifying, assessing, and prioritizing infrastructure risk across the Govern → Identify → Protect → Detect sequence.

NIST AI Risk Management Framework (AI RMF)
Model governance, risk tiering, explainability, and traceability gaps for products with AI components.
What you have at the end of 7 days
A complete map of your compliance exposure—specific to your architecture and regulatory obligations. No generic templates. A structured, actionable blueprint your engineering team can execute immediately.
Every control failure identified and categorized by severity: architecture weaknesses, IAM misconfigurations, encryption gaps, and API vulnerabilities. A detailed technical analysis your team can act on immediately.
Identification of third-party integration risks. Pinpoint which vendors require active BAAs or DPAs and which tools need reconfiguration before your next enterprise security questionnaire.
A clear readiness score against your target framework (SOC 2, HIPAA, ISO 27001, GDPR, or EU AI Act). Benchmarked against actual audit criteria, not a self-reported checklist.
Findings ranked by risk level with engineering effort estimates. Clear prioritization shows what to fix first, what can wait, and exactly where to start.
For AI-based products: an architecture-level review of model lineage gaps, decision logging failures, EU AI Act risk tiers, and GDPR automated decision-making obligations.
A live, technical walkthrough of every exposure point with the assessing engineer. An engineering-to-engineering conversation about your specific system.
Trusted by growing companies, past the MVP stage
Check out what they have to say about working with us.
“They’ve understood the project much better than anyone else and been able to implement quick solutions.”
Corpsoft.io has excelled at quickly delivering, testing features, and finding bugs, making them a great MVP development partner. The team is budget-conscious and offers top-notch project management. Additionally, they’re very agile, available, understanding, and highly communicative.
"Corpsoft.io team delivers quickly."
Corpsoft.io has successfully delivered the custom product using 7.5 sprints, meeting the client's business goals. The team delivers quickly and provides daily updates and weekly video conferences. They ask tough questions and respond to every single comment or question.
“We could mention their technical expertise and wonderful work, but communication is their most impressive trait.”
The client has saved $200,000 and gained an incalculable amount of new business thanks to the platform’s efficiency and professional look. Corpsoft.io has delivered outstanding work, but they’ve excelled overall in project management. They use SCRUM sprints and Jira and are responsive partners.
"The quality of their work was great and they were true thought-partners on the product itself. "
Corpsoft.io even sourced put external experts to work on the project, and their work made a significant difference. Although the business model never took hold, the team provided good quality work.
"They provide regular updates that were easy to understand and the quality of work was amazing."
The client felt like Corpsoft.io was in their own team. Their workflow was easy to understand, even as the client would describe their quality of work as amazing. Overall, the client felt no need for improvement.
"They respond to everything in a practical manner and in a quick time."
Thanks to Corpsoft.io's engagement, they have successfully created a functional app installed with extra features according to what they have agreed with the clients. The team has established effective communication to respond quickly and provide progress updates. They're prompt and structured.
"It is a pleasure working with them."
Corpsoft.io team is professional and highly knowledgeable. They deliver on time after extensive QA process.
Check out what they have to say about working with us.
“They’ve understood the project much better than anyone else and been able to implement quick solutions.”
Corpsoft.io has excelled at quickly delivering, testing features, and finding bugs, making them a great MVP development partner. The team is budget-conscious and offers top-notch project management. Additionally, they’re very agile, available, understanding, and highly communicative.
"Corpsoft.io team delivers quickly."
Corpsoft.io has successfully delivered the custom product using 7.5 sprints, meeting the client's business goals. The team delivers quickly and provides daily updates and weekly video conferences. They ask tough questions and respond to every single comment or question.
“We could mention their technical expertise and wonderful work, but communication is their most impressive trait.”
The client has saved $200,000 and gained an incalculable amount of new business thanks to the platform’s efficiency and professional look. Corpsoft.io has delivered outstanding work, but they’ve excelled overall in project management. They use SCRUM sprints and Jira and are responsive partners.
"The quality of their work was great and they were true thought-partners on the product itself. "
Corpsoft.io even sourced put external experts to work on the project, and their work made a significant difference. Although the business model never took hold, the team provided good quality work.
"They provide regular updates that were easy to understand and the quality of work was amazing."
The client felt like Corpsoft.io was in their own team. Their workflow was easy to understand, even as the client would describe their quality of work as amazing. Overall, the client felt no need for improvement.
"They respond to everything in a practical manner and in a quick time."
Thanks to Corpsoft.io's engagement, they have successfully created a functional app installed with extra features according to what they have agreed with the clients. The team has established effective communication to respond quickly and provide progress updates. They're prompt and structured.
"It is a pleasure working with them."
Corpsoft.io team is professional and highly knowledgeable. They deliver on time after extensive QA process.
See the assessment in action
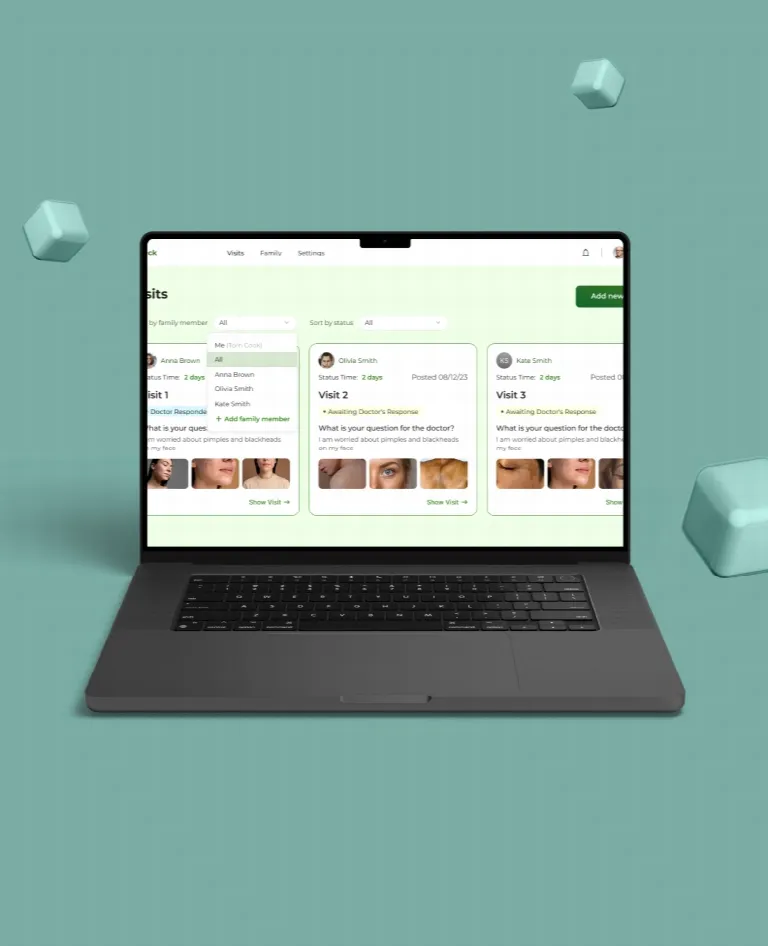
AI-powered dermatology platform built to handle sensitive patient data securely
Handling sensitive patient images without data leakage
Ensuring HIPAA-compliant AI diagnostics
Fragmented dermatology workflows across tools
Slow diagnosis and long patient wait times
Secure image processing with encryption and audit trails
HIPAA-aligned architecture with governed AI models
Unified platform for end-to-end dermatology workflows
AI-assisted diagnostics to accelerate doctor decisions
- Secure, compliant AI diagnostics (HIPAA-aligned)
- End-to-end dermatology workflow in one platform
- 1.5x faster diagnosis & 1–2 minute review time
- Up to 4x reduction in patient wait times
Questions clients ask before we start
The basics
Basic questions about Corpsoft Solutions.
We're a full-service software development company. We build complete platforms, including web apps and AI systems, with compliance engineered in from day one. Think of us as your development team that happens to be compliance experts.
Yes. We start with an architecture and security review of what you already have, then build on top of it rather than starting from scratch.
No — we pick the stack that fits your product and compliance requirements, not the other way around. We work across modern web, mobile, and cloud-native ecosystems.
Pricing depends on scope, timeline, and compliance requirements. Talk to us for an estimate tailored to your project.
Contact
How to reach us and what to expect.
Email or book a call directly — a founder responds personally to every first inquiry, not a sales queue.
Most teams are on a call within 2-3 business days of first reaching out.
Yes, a first call to understand your product and compliance needs costs nothing and comes with no obligation.
Always, before any technical or business detail is shared, if you need one.
Ready to discuss your project with us?Not sure where to start?
Drop us a line about your project or challenge — we'll take it from there.
 Typical response time1 hour on business days