ISO 27001 Compliant Software Development
Architecture that passes an ISO 27001 audit, not just a checklist.
Your product gets ISO 27001 Annex A requirements built into its architecture, from access management and logging to supplier security. An accredited auditor issues the certificate, and our engineers build everything that auditor reviews.
 100% audit readiness
 6 compliance frameworks
 Built for accredited certification
 Global Team Coverage
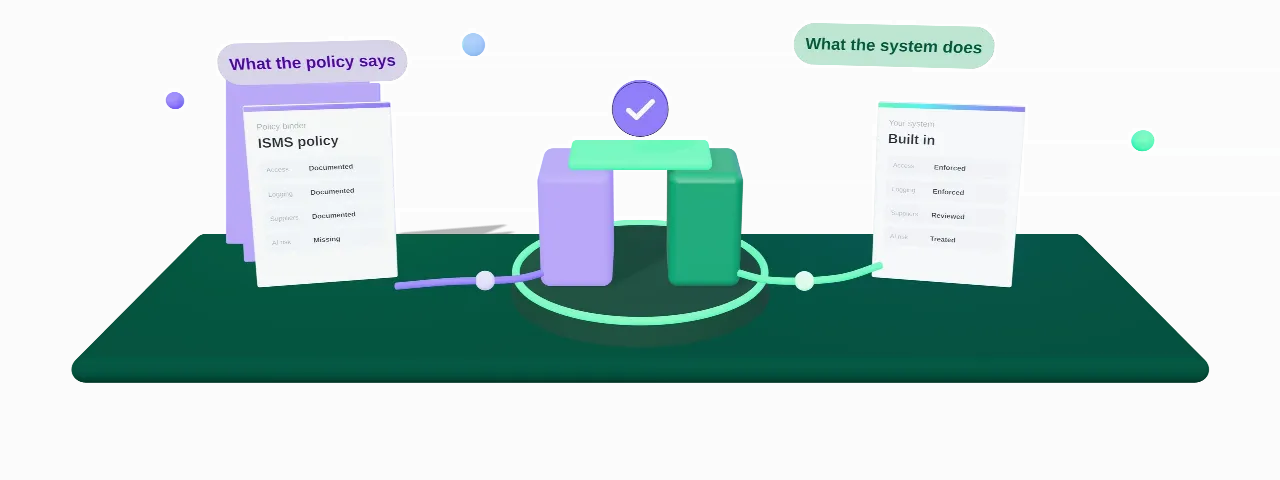
Most ISO 27001 gaps live between the policy and the system.
An ISO 27001 policy describes what your ISMS should do. The system determines what it actually does. Most teams find the gap during a gap analysis, an enterprise vendor review, or a certification audit, when the fix costs more than building it right would have.
Policy doesn't match the system
Our policy binder doesn't match what the system actually does.
A report, but no controls
A consultant sold us a report. Nobody built the controls in it.
AI features left untreated
Our AI features have no documented risk treatment at all.
Buyers demand ISO 27001
Every enterprise buyer now asks for ISO 27001 before they'll sign.
What ISO 27001 compliance services actually cover
ISO 27001 compliance services mean building the Information Security Management System an accredited auditor certifies, not writing a policy that describes one. We map which Annex A controls apply to your system, then design access control, encryption, and risk treatment so the ISMS holds up under a certification audit.
ISO 27001 Gap Analysis
A technical audit of your architecture against every applicable Annex A control, delivering a prioritized gap report and a realistic path to certification readiness.
ISMS Implementation
Engineering the ISMS controls Annex A requires into production: access control, encryption, logging, supplier risk, and incident response, implemented, not just documented.
AI Risk Treatment for ISO 27001
Model risk treatment, access logging, and documented AI-specific controls, so AI features are covered by the same ISMS as the rest of your architecture.
Documentation and Evidence Package
The full policy and evidence library a certification audit requires, written to match your actual implemented controls, not a generic template.
What working with Corpsoft Solutions looks like in numbers
100%
Audit readiness rate
Every Annex A requirement we build comes with logs, evidence and documentation, so your product is ready for review by an accredited ISO 27001 auditor.
5.0
Rating on Clutch
Across 20+ verified client reviews in healthcare, AI and enterprise SaaS.
Related case study:
Clutch profile
6
Core regulations and standards
ISO 27001, HIPAA, SOC 2 Type II, GDPR, EU AI Act and NIS2, built into your product’s architecture from the first sprint.
Related case study:
See other compliance services7 days
Free risk assessment
A prioritized map of the gaps between your ISMS policy and what your system actually does, with what to fix first.
Related case study:
Learn moreSee what ISO 27001-ready architecture looks like for your product.
A discovery call maps your systems against Annex A, checks which controls you already have, and outlines what ISO 27001-ready architecture looks like before the first design decision is made.
Book a Discovery CallHow we build toward ISO 27001 certification
- 01
Annex A Mapping
We map every applicable Annex A control against your architecture, before any implementation decision is made.
- 02
Controls Design
Access control, encryption, and risk treatment are designed against the mapped controls, not handled as one generic policy.
- 03
Implementation
The ISMS is built as working controls in production, with logging and monitoring generating evidence from day one.
- 04
Validation
We test the system against Annex A requirements: control verification and gap analysis before you engage a certification body.
- 05
Evidence & Support
Documentation and audit evidence are generated continuously, and the ISMS is extended as your systems and risks change.
What you have when the engagement is complete
Every deliverable is something you can hand to a certification auditor or your own engineering team, not a slide deck.
ISMS Architecture Blueprint
System diagrams mapped to the Annex A controls they satisfy, covering access, encryption, and data flows, ready for a certification auditor's review.
AI Risk Documentation
Model risk treatment and access logging for AI features, built into the same ISMS as the rest of your architecture, not a separate track.
Audit Evidence Trail
Gap analysis documentation and continuous audit evidence generated from production, not assembled the week before a certification audit.
ISMS Gap Assessment
An honest account of what's covered and what remains open, so nothing surfaces as a surprise during the certification audit.
Trusted by growing companies, past the MVP stage
Check out what they have to say about working with us.
“They’ve understood the project much better than anyone else and been able to implement quick solutions.”
Corpsoft.io has excelled at quickly delivering, testing features, and finding bugs, making them a great MVP development partner. The team is budget-conscious and offers top-notch project management. Additionally, they’re very agile, available, understanding, and highly communicative.
"Corpsoft.io team delivers quickly."
Corpsoft.io has successfully delivered the custom product using 7.5 sprints, meeting the client's business goals. The team delivers quickly and provides daily updates and weekly video conferences. They ask tough questions and respond to every single comment or question.
Check out what they have to say about working with us.
“They’ve understood the project much better than anyone else and been able to implement quick solutions.”
Corpsoft.io has excelled at quickly delivering, testing features, and finding bugs, making them a great MVP development partner. The team is budget-conscious and offers top-notch project management. Additionally, they’re very agile, available, understanding, and highly communicative.
"Corpsoft.io team delivers quickly."
Corpsoft.io has successfully delivered the custom product using 7.5 sprints, meeting the client's business goals. The team delivers quickly and provides daily updates and weekly video conferences. They ask tough questions and respond to every single comment or question.
How our clients got ISO 27001-ready platforms for sensitive data
Patient records, medical images, personal identifiers: these platforms handle the data that needs the strongest protection. Each one was built with the encryption, audit trails and access rules an ISO 27001 auditor reviews.
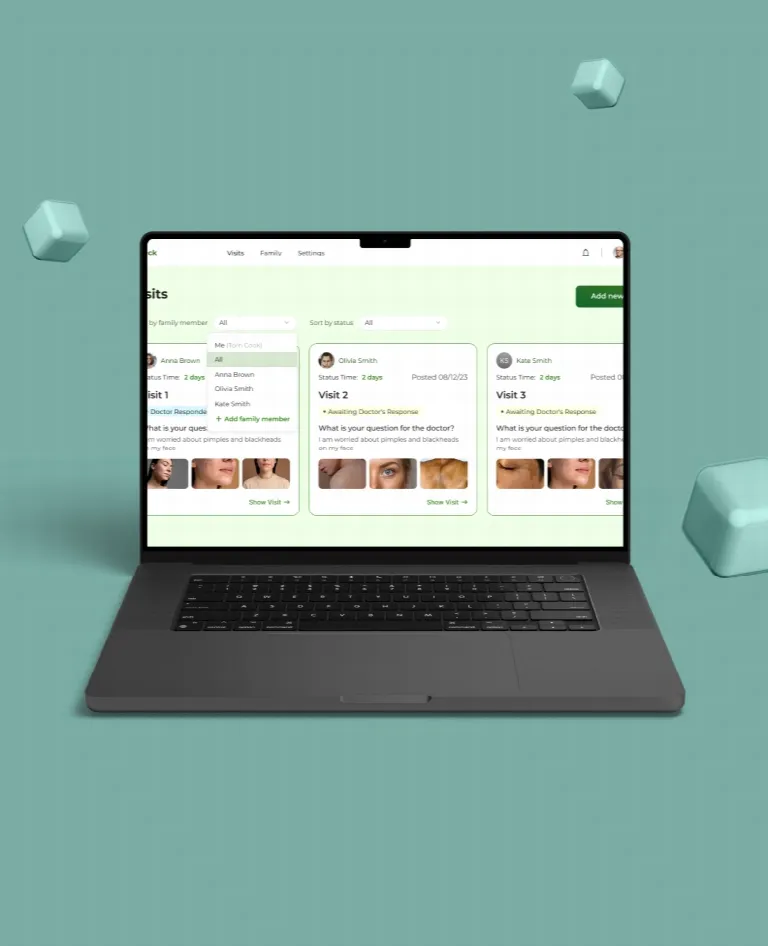
AI-powered dermatology platform built to handle sensitive patient data securely
Handling sensitive patient images without data leakage
Ensuring HIPAA-compliant AI diagnostics
Fragmented dermatology workflows across tools
Slow diagnosis and long patient wait times
Secure image processing with encryption and audit trails
HIPAA-aligned architecture with governed AI models
Unified platform for end-to-end dermatology workflows
AI-assisted diagnostics to accelerate doctor decisions
- Secure, compliant AI diagnostics (HIPAA-aligned)
- End-to-end dermatology workflow in one platform
- 1.5x faster diagnosis & 1–2 minute review time
- Up to 4x reduction in patient wait times
Vehicle SaaS grew registrations 3x with a verified car marketplace
Fragmented vehicle history and ownership data
Trust in online car sales between strangers
Connecting vehicle owners with service providers
Separating consumer and business provider accounts
VIN decoding with vehicle history from external APIs
Photo-based ownership checks and verification badges
Service request flow between owners and providers
Role-based accounts with isolated business data
- 3x more user registrations after launch
- Car listings with verified ownership badges
- Free basic tracking and a subscription tier for advanced features
- Affiliate program connecting local dealerships
Build it ISO 27001-ready once. Certify whenever you're ready.
Tell Andrii what your system does and which standards you’re targeting. In a 30-minute call, he’ll outline the architecture that gets you there.
Book a call with AndriiBuild it ISO 27001-ready once. Certify whenever you're ready.
Tell Andrii what your system does and which standards you’re targeting. In a 30-minute call, he’ll outline the architecture that gets you there.
Book a call with Andrii
Andrii Svyrydov
Founder & CEO of Corpsoft Solutions · ex-Head of Tech at a software company with 1,500+ delivered projects
Further reading on this topic
 September 30, 202610 min read
HIPAA-Compliant LLM Features: What Has to Be True Before You Ship
What a HIPAA-compliant LLM feature has to satisfy before a hospital review, across all three governance layers at once.
View more
 June 20, 202511 min read
What Business Leaders Need to Know About Cutting SaaS Waste Without Blocking Growth
Think you only pay for needed SaaS subscriptions? Hidden costs and forgotten services may be draining your budget and slowing growth.
View more November 19, 202515 min read
GxP from ISO and FDA: What You Need to Know for GxP Compliance in Healthcare
Learn about GxP meaning in healthcare and how digital solutions help you meet GxP standard requirements and maintain compliance.
View more


Questions clients ask before we start
No. Corpsoft Solutions is not an accredited certification body, and no engineering partner can certify your own work. We design and implement the architecture, controls, and evidence trail your Information Security Management System requires: access control, encryption, logging, and risk treatment, so your system passes review on the first attempt. The formal certification audit is still performed by an independent accredited certification body, separate from our engineering work.
Any company selling into enterprise or government accounts, especially in Europe, the UK, or the Middle East, where ISO 27001 is often the default security benchmark procurement teams expect. It's also common for SaaS companies competing for deals where a US buyer might accept SOC 2 but an international buyer specifically asks for ISO 27001. If your sales team keeps hearing the same question from a specific region, that's usually the signal.
A technical review of your architecture against every applicable Annex A control: access management, cryptography, physical security, supplier relationships, incident management, and business continuity, among others. The output is a prioritized gap report, not a generic checklist, showing exactly which controls are missing, partially in place, or already sufficient, with a realistic path to audit readiness.
The gap analysis takes about a week. Full implementation typically runs 8 to 16 weeks, depending on the number of gaps and the complexity of your existing architecture. The certification audit itself, run by an accredited body, is a separate process and timeline that starts once your ISMS has been operating long enough to generate evidence. Corpsoft Solutions provides a specific schedule after the gap analysis.
Ready to discuss your project with us?Not sure where to start?
Drop us a line about your project or challenge — we'll take it from there.
 Typical response time1 hour on business days