GDPR-Compliant Software Development
Personal data handled the way GDPR requires, from the first release.
Your product gets GDPR controls for US, UK and EU users, including AI decisions covered by Article 22 and the EU AI Act.
 100% audit readiness
 6 frameworks built in
 UK GDPR & EU GDPR coverage
 Data protection by design (Art. 25)
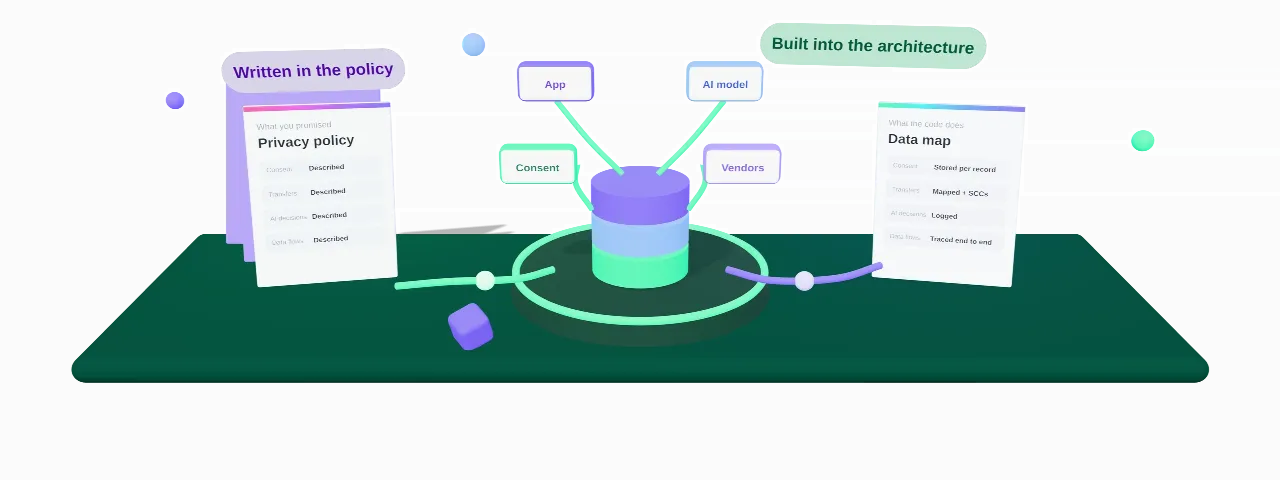
Most GDPR gaps live in the architecture, not the policy.
GDPR describes what your system must do with personal data. The code determines what it actually does. Most teams find the gap during a DPIA, an enterprise vendor review, or a regulator's request, when the fix costs far more than building it right would have.
Unmapped data flows
No one can show where personal data actually flows.
Consent in the wrong place
Consent logic lives in a form, not the database.
Unexplained AI decisions
AI features make decisions no one can fully explain.
Unmapped transfers
Every new market adds a data transfer no one mapped.
What we build to
Corpsoft Solutions builds GDPR-compliant software to the requirements regulators and enterprise buyers actually check, not a generic privacy policy template.
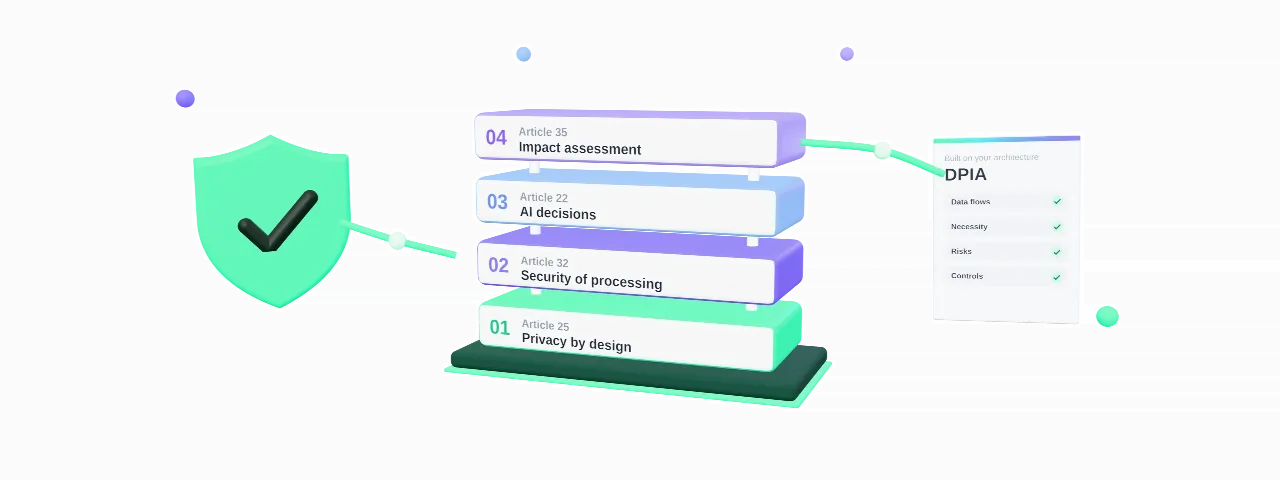
01
GDPR Article 25 — Privacy by Design and by Default
Data protection measures built into the architecture from the start, not added as a configuration option after launch.
02
GDPR Article 32 — Security of Processing
Encryption, access control, and the ability to restore availability after an incident, implemented as architectural requirements.
03
GDPR Article 22 — Automated Decision-Making
Human review, explanation, and the right to contest a decision, built into any AI feature that decides something about a person.
04
GDPR Article 35 — Data Protection Impact Assessment
Documentation generated from the architecture itself for any high-risk processing, not written from memory before a deadline.
What GDPR-compliant software development actually means
GDPR-compliant software development means building systems where data protection is a structural decision, not a policy attached afterward. We map which GDPR articles apply to your product, then design consent flows, data minimization, and access controls so the system holds up under a DPIA or a regulator's request.
GDPR Compliance for AI Features
Model lineage, a documented lawful basis, and human review built into any AI feature that scores, ranks, or decides something about a person.
Build vs. Buy: GDPR Software
A working session on whether your product needs GDPR-compliant software built in, or whether an existing compliance tool actually covers your case.
GDPR-Compliant Web Development
Cookie consent, data subject request handling, and secure forms built into your website from the first sprint, not patched in before a launch.
What we find in software built without GDPR in mind
No lawful basis
Personal data shows up in logs, backups, or analytics tools no one added a lawful basis for.
Consent checked once
Consent is collected once at signup and never checked again when the product changes.
Unexplainable AI
An AI feature scores or ranks people, and no one can explain the logic behind a single decision.
No transfer mechanism
Data sits on a US server with no transfer mechanism on file, because no one owns that question.
Logs without answers
Access logs exist, but no one can say who touched a specific record, or why.
What working with Corpsoft Solutions looks like in numbers
100%
Audit readiness
Across our GDPR engagements. If our architecture contributes to a failed review, we fix it as part of the engagement.
5.0
Rating on Clutch
Across 20+ verified client reviews in healthcare, AI and enterprise SaaS.
6
Compliance frameworks
Built into your product’s architecture as needed: GDPR, HIPAA, SOC 2 Type II, ISO 27001, EU AI Act and NIS2.
72 hours
To report a breach
GDPR’s deadline for notifying the regulator. Breach detection and incident logs are built so your team can meet it.
See what GDPR-compliant architecture looks like for your product.
A discovery call maps your data flows, checks which articles apply across US, UK, and EU users, and outlines what GDPR-compliant architecture looks like for your system before the first design decision is made.
Book a Discovery CallHow we build GDPR-compliant software
- 01
Data Mapping
We map every place personal data enters, moves through, or leaves your system, before any architecture decision is made.
- 02
Lawful Basis Design
Consent, contract, and legitimate interest are mapped to specific data flows, not handled as one blanket policy.
- 03
Architecture Build
Access controls, encryption, and data minimization are built as requirements from the start, not added after a review.
- 04
AI & Automated Decisions
Model logic, human review points, and explanation records are built into any feature that decides something about a person.
- 05
Evidence & Support
DPIA documentation and audit evidence are generated continuously, and the architecture is extended as guidance changes.
What you have when the engagement is complete
Every deliverable is something you can hand to a regulator, a data protection officer, or your own engineering team, not a slide deck.
Data Protection Architecture
System diagrams mapped to the GDPR articles they satisfy, covering data flows, storage, and third-party transfers, ready for a DPO or auditor's review.
AI Decision Documentation
Model lineage, human review points, and explanation records for any AI feature that makes or supports a decision about a person.
DPIA & Evidence Package
Data protection impact assessment documentation and audit evidence generated from production, not assembled the week before a review.
International Transfer Mapping
Every cross-border data flow reviewed against the current transfer mechanism, so a US, UK, or EU deal doesn't stall on paperwork.
Trusted by growing companies, past the MVP stage
 |20+ reviews
5★/21
Check out what they have to say about working with us.
“We could mention their technical expertise and wonderful work, but communication is their most impressive trait.”
The client has saved $200,000 and gained an incalculable amount of new business thanks to the platform’s efficiency and professional look. Corpsoft.io has delivered outstanding work, but they’ve excelled overall in project management. They use SCRUM sprints and Jira and are responsive partners.
"Corpsoft.io team delivers quickly."
Corpsoft.io has successfully delivered the custom product using 7.5 sprints, meeting the client's business goals. The team delivers quickly and provides daily updates and weekly video conferences. They ask tough questions and respond to every single comment or question.
|20+ reviews5★/21
Check out what they have to say about working with us.
“We could mention their technical expertise and wonderful work, but communication is their most impressive trait.”
The client has saved $200,000 and gained an incalculable amount of new business thanks to the platform’s efficiency and professional look. Corpsoft.io has delivered outstanding work, but they’ve excelled overall in project management. They use SCRUM sprints and Jira and are responsive partners.
"Corpsoft.io team delivers quickly."
Corpsoft.io has successfully delivered the custom product using 7.5 sprints, meeting the client's business goals. The team delivers quickly and provides daily updates and weekly video conferences. They ask tough questions and respond to every single comment or question.
How our clients keep personal data GDPR-ready at scale
More users means more personal data to protect. These platforms grew while access stayed limited by role and every data flow stayed documented and traceable.
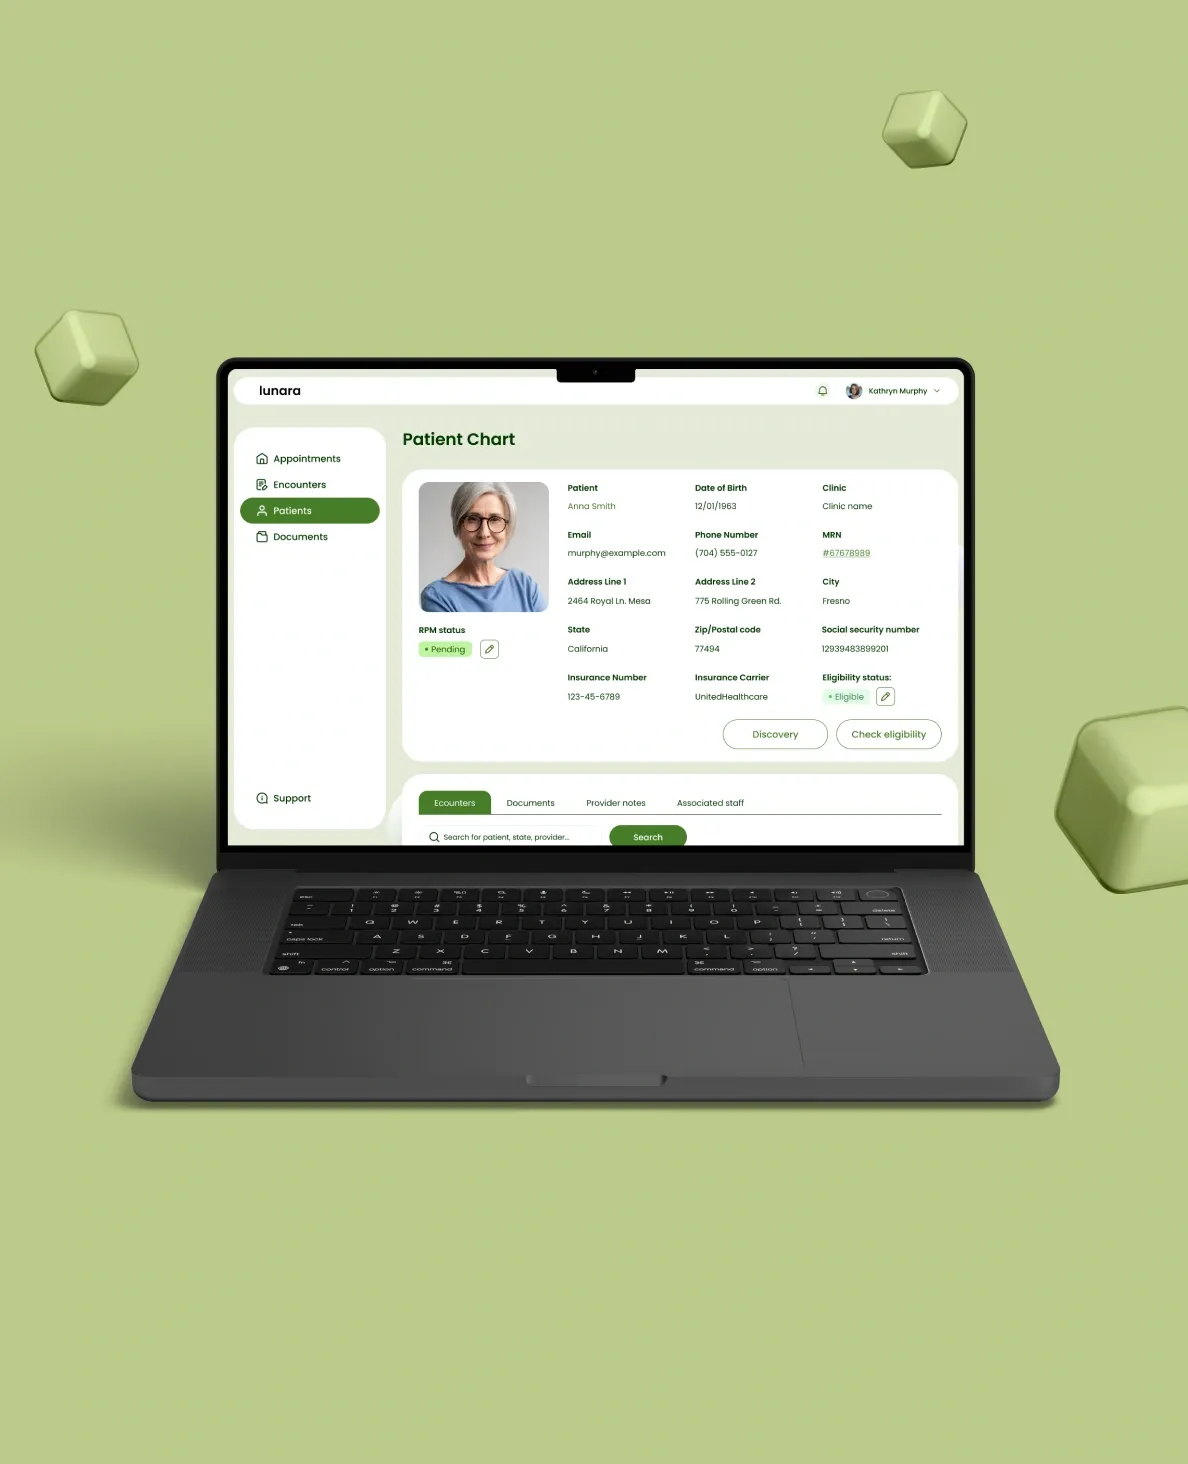
Comprehensive Remote Patient Monitoring Platform for Chronic Care Management
Manual follow-ups and referrals overloading care teams
Tracking cognitive health remotely between visits
Securing patient data across four user roles
Automated patient journeys and provider scheduling
Built-in cognitive assessments with scheduled retests
HIPAA-compliant SSO with RBAC and audit logging
- 60% reduction in administrative workload
- Continuous remote monitoring of chronic conditions
- Role-based access for patients, providers, therapists, and admins
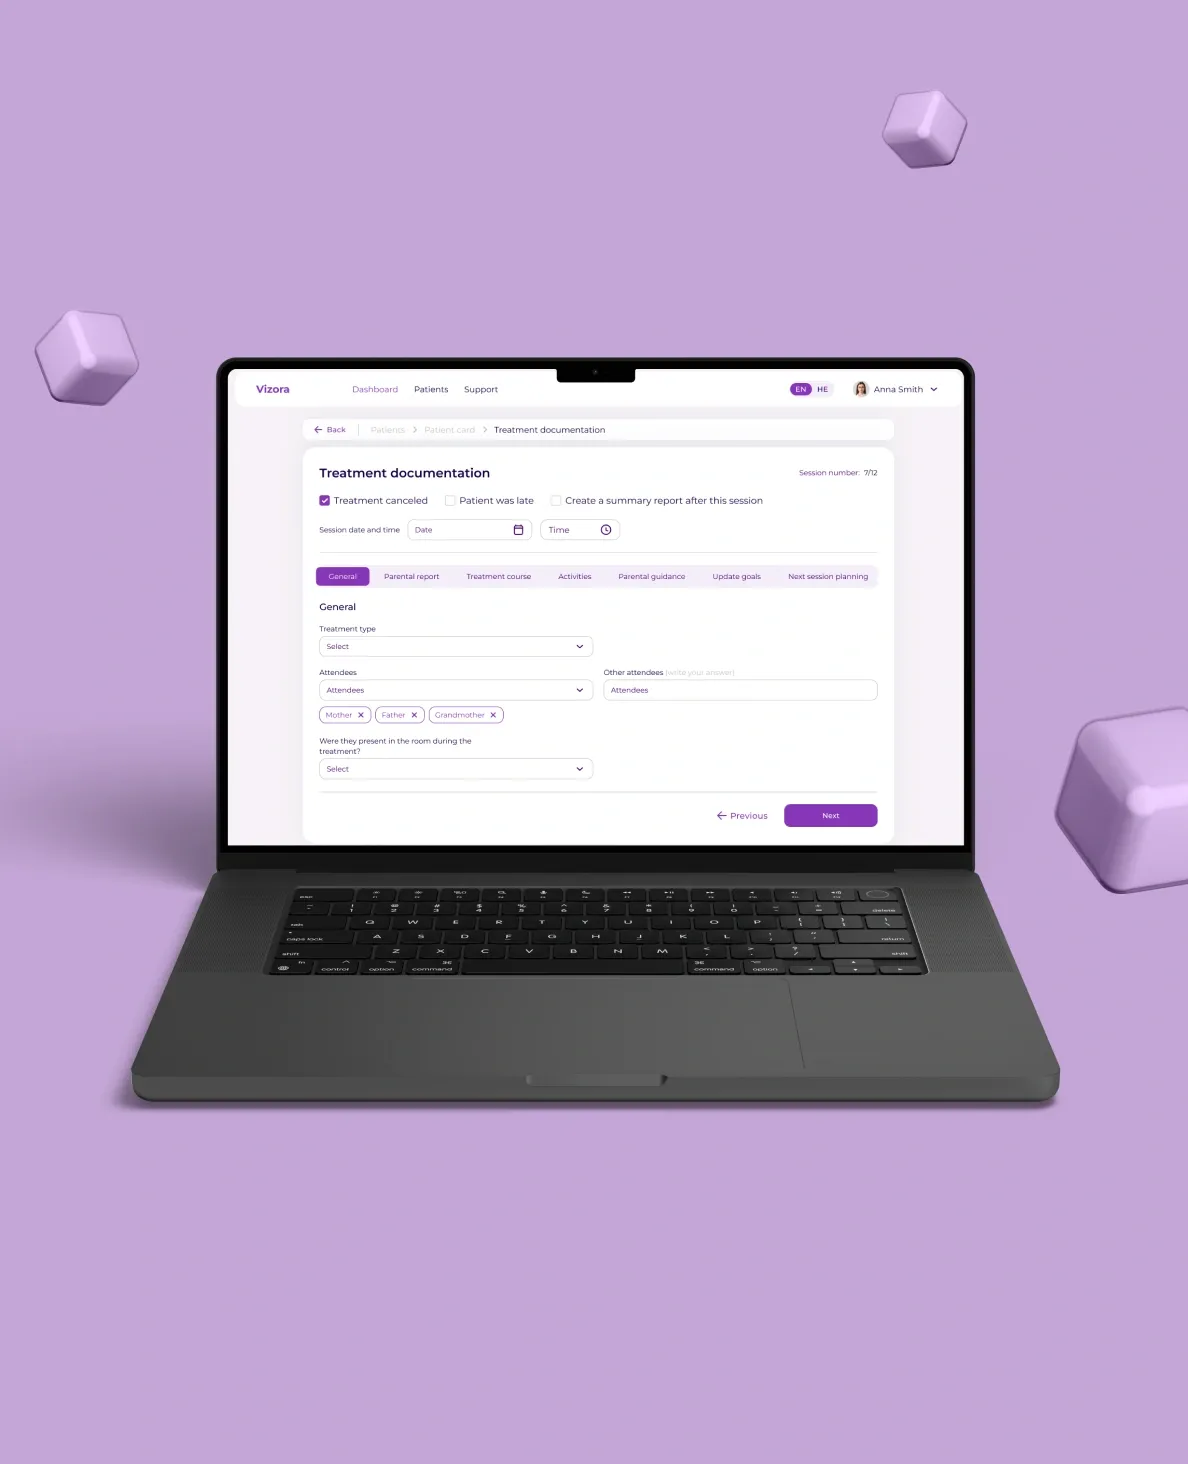
A Revolutionizing Platform For Pediatric with AI-Powered Workflow Optimization
Paperwork and slow access to patient data
Protecting patient data processed by AI
AI summaries and two-click access to patient records
Encrypted PHI storage with role-based access controls
- Treatment summary reports cut from 45 to 5 minutes
- Fully digital patient registration and records
- More time for patient care and higher daily capacity
- Real-time dashboard tracking time saved
Build it GDPR-compliant once. Reuse it in every new market.
Tell Andrii where your users are and what you’re building. He’ll outline the architecture in a 30-minute call.
Book a Discovery Call with AndriiBuild it GDPR-compliant once. Reuse it in every new market.
Tell Andrii where your users are and what you’re building. He’ll outline the architecture in a 30-minute call.
Book a Discovery Call with Andrii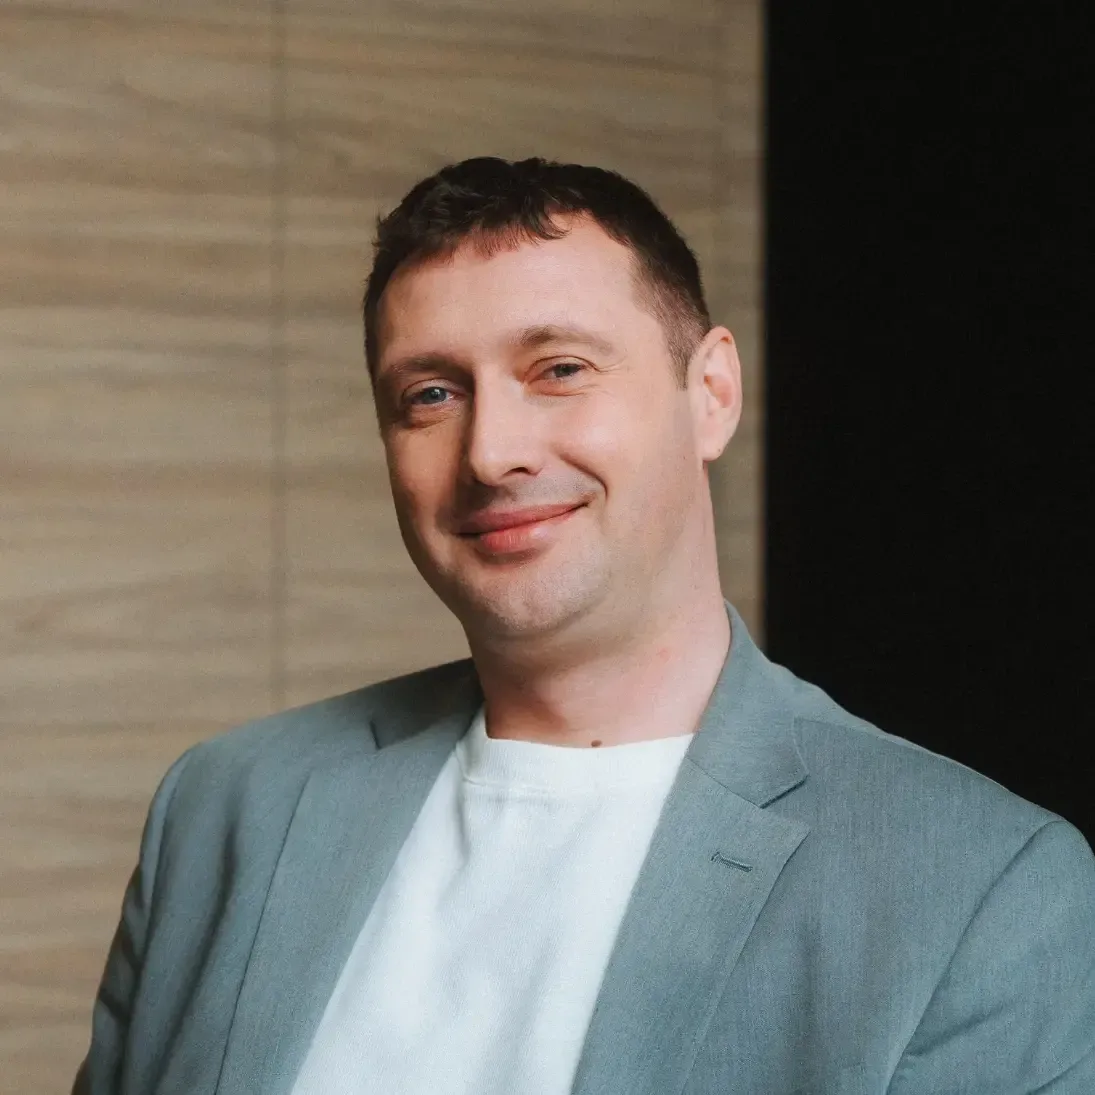
Andrii Svyrydov
Founder & CEO of Corpsoft Solutions · ex-Head of Tech at a software company with 1,500+ delivered projects
Further reading on this topic
 July 17, 202620 min read
GDPR-Compliant AI: What Engineers Need to Log, Trace, and Explain
GDPR doesn't just require a privacy policy — it requires an audit trail. Here's what to log, trace, and explain in AI systems processing personal data.
View more
 February 19, 202619 min read
Website GDPR Compliance: How to Check and What to Fix
Learn what makes a GDPR-compliant website and how to achieve it with our detailed action plan
View more June 19, 202613 min read
EU AI Act Explained: What Your System Must Actually Do
EU AI Act compliance deadlines hit in 2026 and 2027. Learn which risk tier your AI falls into and what AI systems must actually do.
View more


Questions clients ask before we start
It means building your system so data protection is a structural decision, not documentation added afterward. In practice, that covers a documented lawful basis for every use of personal data, data minimization by design, encryption, access controls, and the ability to produce evidence for a DPIA or a regulator on request. We map the applicable articles before writing architecture decisions, then build the system to hold up under review.
UK GDPR is nearly identical to EU GDPR in substance, enforced separately by the Information Commissioner's Office (ICO) rather than an EU data protection authority. A product serving both markets generally needs one architecture that satisfies both regimes, with attention to the specific points where UK guidance has diverged since Brexit. We build to both from the same codebase, not as two separate compliance tracks.
Depends on what you're protecting. A GDPR compliance platform can manage internal processes like consent records or vendor risk. It cannot make your own product's data flows, AI features, or user-facing consent logic compliant, because that lives in your codebase, not a dashboard. Most teams end up needing both: a tool for internal governance, and an architecture that's compliant by design.
Yes. HIPAA and GDPR overlap heavily on encryption, access control, and audit logging, but GDPR adds requirements HIPAA doesn't have, like a documented lawful basis and data subject rights such as erasure. We map both frameworks into a single architecture rather than treating them as separate projects, the same approach covered on our HIPAA-compliant software development page.
Usually yes. GDPR applies extraterritorially to any organization that processes personal data belonging to people in the EU or UK, regardless of where the company is based. If your product has EU or UK users, or you process their data on behalf of a client that does, GDPR requirements apply to your software even without a physical presence there.
Yes. AI features that score, rank, or make decisions about a person fall under GDPR Article 22 on automated decision-making, and increasingly under the EU AI Act as well. We build model lineage, human review points, and explanation records into these features from the start, using the same approach behind our AI governance services.
The core areas are lawful basis, data minimization, consent and data subject rights, encryption and access control, DPIA triggers, and international transfer mechanisms. For software specifically, that also means consent logic built into the product itself, not just a cookie banner, and a way to actually fulfill a deletion or access request when one comes in.
Ready to discuss your project with us?Not sure where to start?
Drop us a line about your project or challenge — we'll take it from there.
 Typical response time1 hour on business days