SOC 2 Type II Compliant Software Development
Get SOC 2 ready without pausing your roadmap.
Your product gets the security controls, audit evidence and documentation enterprise buyers require, built into its architecture. From gap assessment to Type II readiness, engineering keeps shipping.
 AWS Partner, Select Tier
 SOC 2 · ISO 27001 · GDPR · HIPAA
 Free 7-day gap assessment
 Controls ready for the observation period in 90 days
An enterprise deal blocked on SOC 2 does not wait six months.
Enterprise buyers ask for a SOC 2 Type II report before they sign. Without one, procurement stalls the deal and security reviewers block onboarding. A consultant’s gap analysis tells your team what to build, and an auditor later tells you what’s still missing. The engineering in between is where most teams lose quarters.
Here’s how that sounds:
A stalled enterprise deal
“An enterprise prospect has been waiting on our SOC 2 report for three months. The deal is stalling.”
A report to build from
“We paid a consultant for a gap analysis. Now our engineers have to build everything the report describes.”
Two lost quarters
“Our CTO estimates SOC 2 will take a year and derail two quarters of product work.”
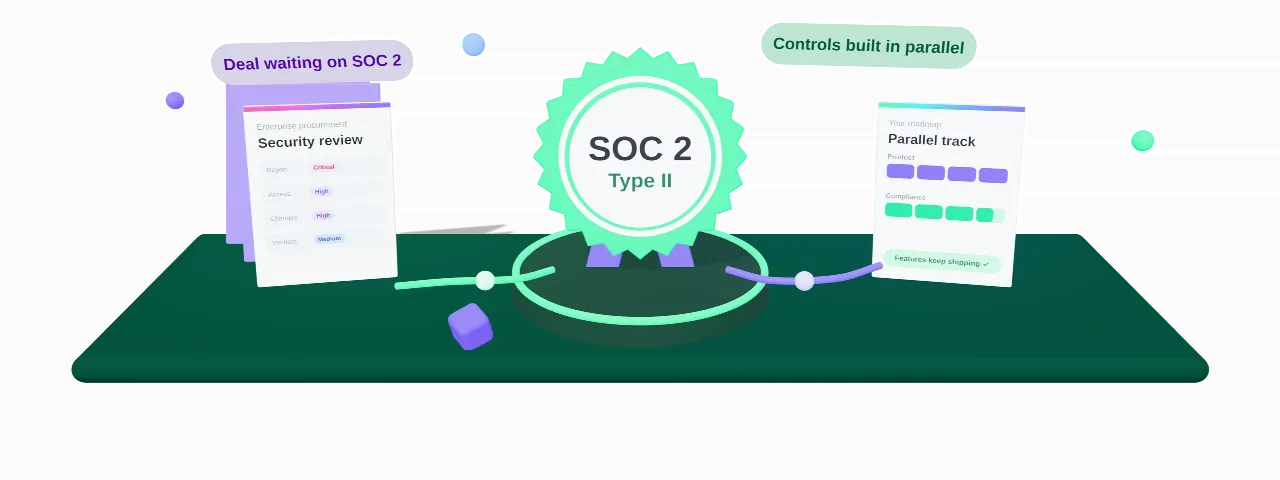
SOC 2 compliance that ships — not compliance that reports.
Corpsoft Solutions implements the security controls SOC 2 Trust Service Criteria require directly in your product architecture. Access controls, encryption, audit logging, system monitoring, incident response, change management, and vendor risk management — engineering-grade implementation that creates real evidence for your CPA auditor, not a policy document describing what you plan to build someday.
SOC 2 Readiness Assessment
A 7-day technical audit of your architecture against all SOC 2 Common Criteria — CC1 through CC9 — plus any additional Trust Service Categories you are pursuing. Delivers a gap report with a prioritized remediation roadmap and a projected timeline to audit readiness.
Security Controls Implementation
Engineering the Common Criteria controls into your production systems: logical access controls, encryption at rest and in transit, network segmentation, system monitoring and alerting, audit
SOC 2 Policy and Procedure Documentation
The full policy library a SOC 2 audit requires: information security policy, access control policy, incident response plan, change management procedures, vendor management policy, business continuity plan, and supporting procedures. Written to match your actual implemented controls — not generic templates.
Audit Evidence Management
Continuous evidence collection throughout the observation period: access logs, change tickets, security alerts, vendor assessments, and control monitoring results — organized in the format your CPA auditor expects. No last-minute evidence scramble before the audit.
Penetration Testing
SOC 2 Type II audits require evidence of vulnerability testing. Corpsoft Solutions coordinates penetration testing through vetted security partners, manages remediation of findings, and packages the results as audit evidence.
Continuous Vulnerability Management
Recurring automated scanning, risk prioritization, and remediation — starting at $200/month. Maintains SOC 2 compliance status post-certification and provides ongoing audit evidence for annual Type II renewals.
What working with Corpsoft Solutions looks like in numbers
7 days
To a gap report
From engagement start to a complete SOC 2 gap report with a prioritized remediation roadmap and projected audit-readiness date.
90
Days to audit-ready
Typical time from gap assessment to audit-ready status. The observation period starts the day controls go into production.
100%
Common Criteria evidenced
Every Common Criteria control implemented and evidenced in each full engagement before the audit window opens.
5.0
Rating on Clutch
Across 20+ verified client reviews in healthcare, AI and enterprise SaaS.
Enterprise deal stalled on SOC 2? We will tell you exactly what it takes to unblock it.
Corpsoft Solutions assesses your current architecture against all SOC 2 Trust Service Criteria and delivers a prioritized remediation roadmap in 7 days — with a realistic timeline to audit readiness that does not cost you two quarters of engineering.
Book a scoping callHow SOC 2 compliance implementation works
- 01
Gap assessment
Seven-day audit of your architecture, access controls, logging, monitoring, change management, vendor relationships, and incident response capability — benchmarked against SOC 2 Common Criteria and your selected Trust Service Categories.
- 02
Remediation roadmap
Prioritized implementation plan with milestones tied to audit risk — critical gaps that would block Type II certification are addressed first. Engineering continues in parallel throughout.
- 03
Controls implementation
Corpsoft Solutions engineers the required security controls into your production systems: access management, encryption, monitoring, logging, incident detection, change controls, and vendor risk management procedures.
- 04
Evidence collection
Continuous collection and organization of audit evidence throughout the observation period — access logs, alert histories, change records, vendor assessments — in the format your CPA auditor expects.
- 05
Audit support
Corpsoft Solutions works alongside your CPA auditor during the Type II assessment: answering technical questions, providing additional evidence, and resolving any control gaps identified during fieldwork.
After SOC 2 implementation
Corpsoft Solutions delivers working controls and continuous evidence — not a compliance plan. After implementation, your systems satisfy SOC 2 Type II requirements in production, your observation period runs without gaps, and your engineering team keeps shipping product throughout.
Enterprise deals unblocked
SOC 2 Type II report answers the security questionnaire that stalled your enterprise prospects — procurement approves, legal signs off, and onboarding proceeds.
Type II audit passed
Controls implemented and evidenced before the observation period opens — your CPA auditor reviews a system that was built for the audit, not retrofitted for it.
Continuous monitoring active
System monitoring, alerting, and incident detection running in production — generating the ongoing evidence SOC 2 Type II renewals require every year.
Vendor risk managed
Third-party vendor assessments complete, security requirements in supplier contracts, and ongoing vendor risk monitoring in place — a frequent finding in unprepared SOC 2 audits, closed before the observation period starts.
Policy library complete
Full set of SOC 2-required policies and procedures — written to match your actual implemented controls, reviewed by the engineers who built them.
Engineering roadmap maintained
Implementation sequenced in parallel with product development — no frozen quarters, no all-hands compliance sprints.
How our clients scaled without losing audit readiness
Every new user, integration and data flow adds risk. In these projects, each one shipped with encryption, access control and logging already in place, so the platform stayed ready for SOC 2 review at every stage of growth.
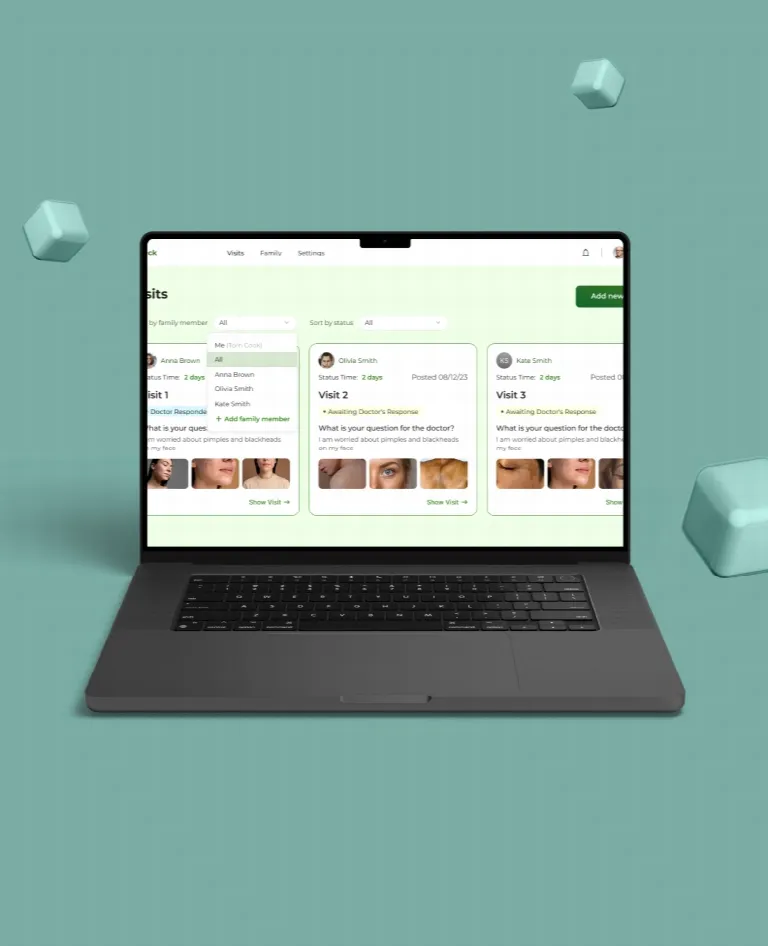
Remote vision testing platform scaled to 10,000+ users with HIPAA and SOC 2 readiness
Outgrown WordPress platform limiting new screening tests
Unreliable validity of remote vision test results
Meeting HIPAA requirements for patient data and access
Manual patient data transfer between clinics and EHRs
Migration from WordPress to a scalable custom stack
Updated test logic with result validation checks
Encrypted PHI storage with RBAC and audit logging
Optometry EHR integration with clinic management tools
- 40% fewer invalid vision test results
- Patient data synced with optometry EHR systems
- HIPAA-compliant data storage with role-based access
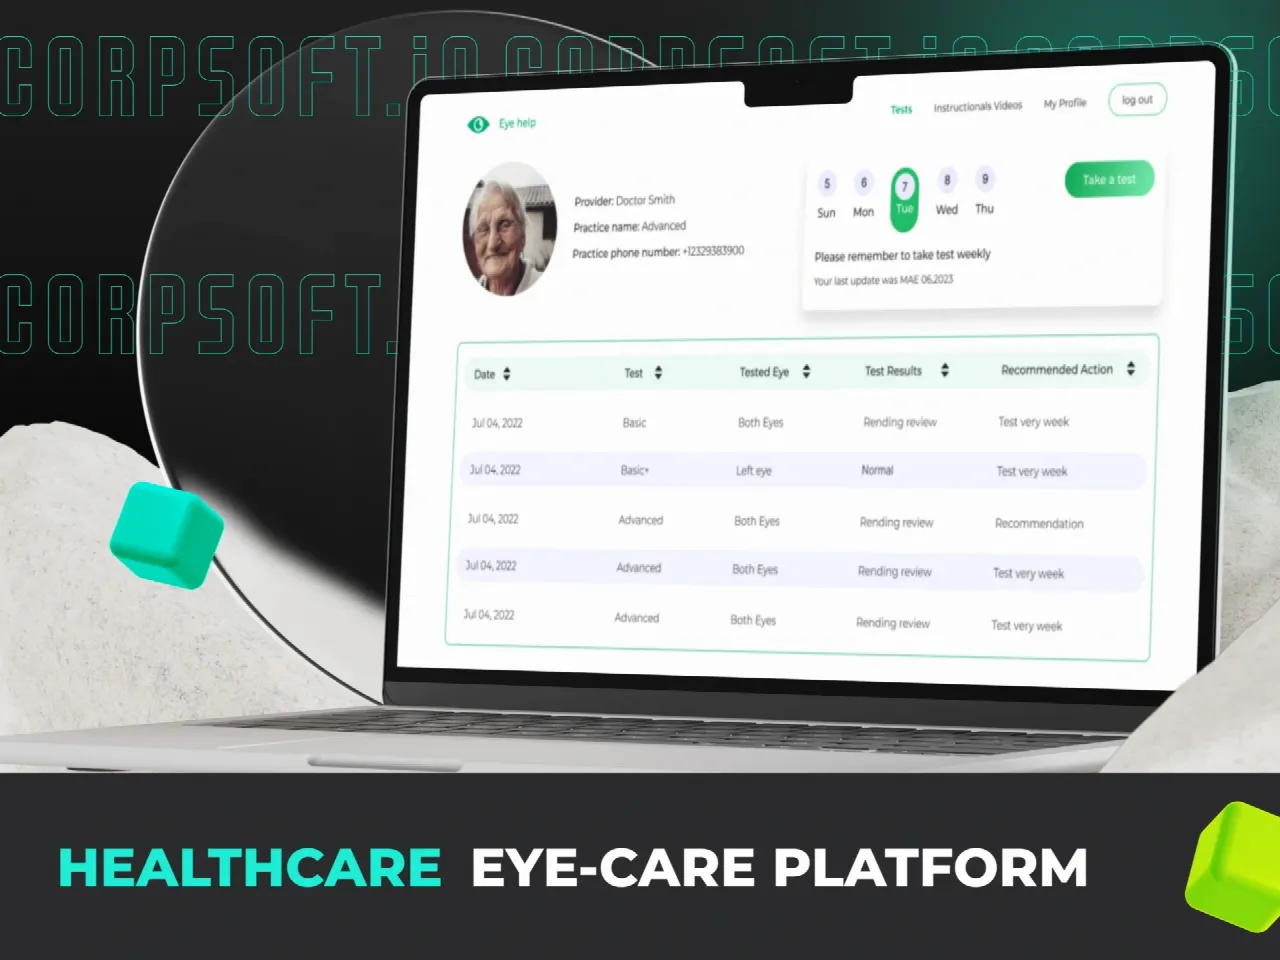
AI-powered dermatology platform built to handle sensitive patient data securely
Handling sensitive patient images without data leakage
Ensuring HIPAA-compliant AI diagnostics
Fragmented dermatology workflows across tools
Slow diagnosis and long patient wait times
Secure image processing with encryption and audit trails
HIPAA-aligned architecture with governed AI models
Unified platform for end-to-end dermatology workflows
AI-assisted diagnostics to accelerate doctor decisions
- Secure, compliant AI diagnostics (HIPAA-aligned)
- End-to-end dermatology workflow in one platform
- 1.5x faster diagnosis & 1–2 minute review time
- Up to 4x reduction in patient wait times
Start with a 7-day SOC 2 gap assessment.
On the call, Andrii will review your architecture against all SOC 2 Trust Services Criteria and deliver a prioritized remediation roadmap with a realistic timeline to audit readiness, planned alongside your product roadmap.
Book a call with AndriiStart with a 7-day SOC 2 gap assessment.
On the call, Andrii will review your architecture against all SOC 2 Trust Services Criteria and deliver a prioritized remediation roadmap with a realistic timeline to audit readiness, planned alongside your product roadmap.
Book a call with Andrii
Andrii Svyrydov
Founder & CEO of Corpsoft Solutions · ex-Head of Tech at a software company with 1,500+ delivered projects
Further reading on this topic
 August 12, 202617 min read
SOC 2 Type II Compliance: What Auditors Actually Expect Your System to Do
SOC 2 Type II auditors don't read your policy docs. They test whether your system's controls actually hold for months.
View more
 April 15, 202621 min read
How to Align Your Global Web Platform with the European Accessibility Act: Key Requirements and Tips for Digital Accessibility in the EU
Make accessibility your competitive edge—streamline your EU market entry and avoid costly rework.
View more October 31, 202512 min read
How Incident Action Plan Software Supports ISO 9001 Quality Management in Healthcare
Think minor errors don’t matter? They do and can cost your clinic its reputation. See how modern incident reporting software helps you prevent disasters.
View more


Ready to discuss your project with us?Not sure where to start?
Drop us a line about your project or challenge — we'll take it from there.
 Typical response time1 hour on business days