FCA Compliant Software Development
Operational resilience the FCA can actually verify, built into your systems.
Your platform gets the technical controls UK-regulated financial firms need under FCA operational resilience rules, outsourcing requirements and Consumer Duty, engineered into the architecture from the start.
 100% audit readiness
 AWS Select Tier Partner
 7-Day Risk Assessment
 Mapped to PS21/3 and SYSC 8
An operational resilience gap doesn't wait for your next audit to become a problem.
The FCA’s operational resilience rules (PS21/3, SYSC 15A) took full effect in March 2025. Regulated firms must already keep important business services within impact tolerances. Consultants define those services and tolerances. The monitoring, failover and incident detection that prove it still have to be built, often by a team that can’t pause product work.
Here’s how that sounds inside the firm:
Mapped, but never built
Our compliance consultant mapped our important business services. Nobody built the systems that keep them inside impact tolerance.
Never tested
We can't tell our board what happens to a critical service during a severe-but-plausible outage, because we've never tested it.
Responsibility stays with you
Our cloud provider handles uptime. The FCA still holds us responsible for the outcome.
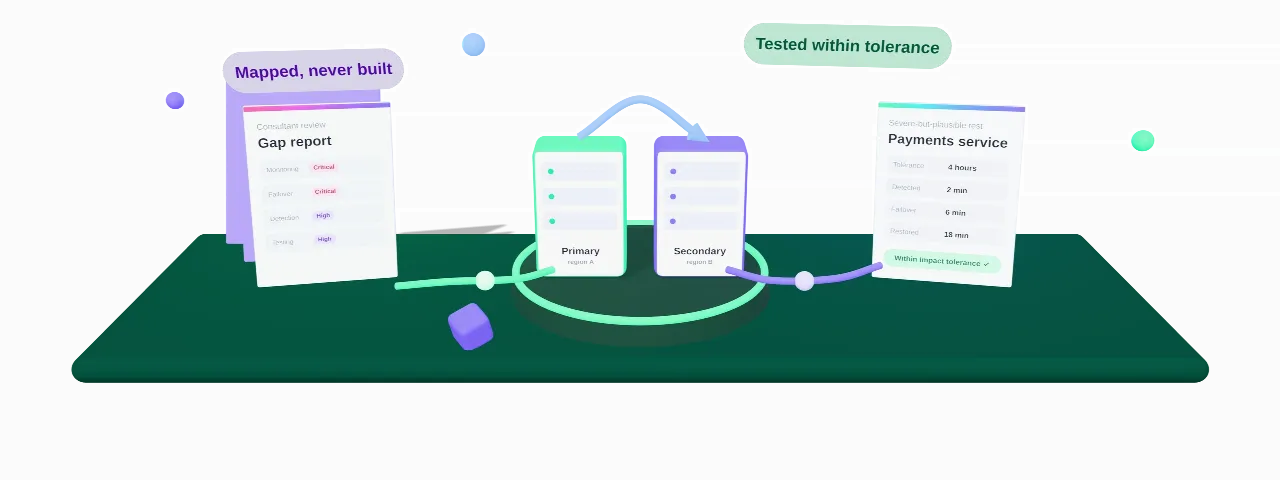
FCA compliance that holds up under a severe-but-plausible test.
Consultants define your important business services and impact tolerances. Our engineers build the systems that keep you inside them, so your team can run them and your board can stand behind them.
Operational Resilience Gap Assessment
A 7-day technical review of your important business services, impact tolerances and the systems behind them, benchmarked against SYSC 15A. Delivers a prioritized remediation roadmap with a realistic timeline.
Resilience Architecture & Monitoring
Monitoring, failover and incident detection that keep important business services within stated impact tolerances, tested against severe-but-plausible scenarios.
Outsourcing & Cloud Risk Implementation
Third-party and cloud dependencies mapped against SYSC 8 and FG16/5, with risk assessment, access rights and exit planning built into your vendor architecture.
Consumer Duty Data & Reporting
Data pipelines and reporting that evidence customer outcomes, built on top of your operational resilience controls.
What working with Corpsoft Solutions looks like in numbers
100%
Audit readiness
Across our compliance engagements. If our architecture contributes to a failed review, we fix it as part of the engagement.
5.0
Rating on Clutch
Verified rating across healthcare, AI and enterprise SaaS engagements.
AWS
Select Tier Partner
Relevant to the cloud and outsourcing risk review most FCA-regulated firms need.
7 days
To a gap report
From engagement start to a complete operational resilience gap report with a prioritized remediation roadmap.
We map your operational resilience gaps in 7 days, before the FCA does.
We review your important business services against FCA operational resilience, outsourcing and Consumer Duty requirements, then deliver a prioritized remediation plan that runs alongside your product roadmap.
Get a 7-Day Gap AssessmentHow FCA compliance implementation works
- 01
Important business service mapping
Identify which services qualify as "important" under SYSC 15A and document the people, process, technology, facilities, and information behind each.
- 02
Gap assessment
Seven-day audit of your current resilience, outsourcing, and data reporting posture against stated impact tolerances and FCA requirements.
- 03
Remediation roadmap
Prioritized plan that separates regulatory-critical gaps from lower-priority improvements, sequenced so engineering continues in parallel.
- 04
Resilience implementation
Monitoring, failover, access control, and incident detection engineered into production systems and tested against severe-but-plausible scenarios.
- 05
Evidence and reporting
Documentation, test results, and monitoring dashboards organized for board review and ready for an FCA request.
What you have once FCA controls are running
Corpsoft Solutions delivers working resilience systems and the evidence behind them. Your important business services are built and tested to stay within stated impact tolerances, and your team can show that to the board or the FCA.
Impact tolerances tested in practice
Monitoring and failover tested against severe-but-plausible scenarios, with results on record.
Outsourcing risk documented and managed
Cloud and third-party dependencies mapped against SYSC 8 and FG16/5, with exit plans in place before a regulator asks for them.
Consumer Duty data evidenced
Reporting that shows customer outcomes alongside service performance.
Board-ready evidence package
Test results, monitoring data and remediation history organized for governance review on demand.
Engineering roadmap maintained
Implementation sequenced in parallel with product development, so feature work keeps moving.
Self-assessment kept current
The technical evidence your annual SYSC 15A self-assessment needs, updated as your systems change.
Start with a 7-day operational resilience gap assessment.
Here’s what the seven days cover: Days 1-2: important business services mapped to the systems behind them Days 3-5: monitoring, failover and third-party dependencies checked against SYSC 15A and SYSC 8 Days 6-7: a prioritized remediation roadmap, walked through with your team.
Start the Assessment with AndriiStart with a 7-day operational resilience gap assessment.
Here’s what the seven days cover: Days 1-2: important business services mapped to the systems behind them Days 3-5: monitoring, failover and third-party dependencies checked against SYSC 15A and SYSC 8 Days 6-7: a prioritized remediation roadmap, walked through with your team.
Start the Assessment with Andrii
Andrii Svyrydov
Founder & CEO of Corpsoft Solutions · ex-Head of Tech at a software company with 1,500+ delivered projects
Further reading on this topic
 July 22, 202513 min read
Are RCM Systems the Hidden Lever to Faster Payments and Business Growth
Tired of hovering contracts and late payments? Implement RCM healthcare solutions to fix your accounting.
View more
 February 24, 202617 min read
AI Agents in Finance: Evaluating the Path from Automation to Autonomy
Learn how AI agents expand the capabilities of financial institutions and improve ROI
View more June 16, 202511 min read
How AI Audit Software Finds Financial Losses Your Team Misses
What AI Audit Software can do? Discover a system that detects losses even the most experienced team might miss.
View more


Questions clients ask before we start
Under SYSC 15A, regulated firms must identify their important business services, the ones whose disruption could cause intolerable harm to consumers or threaten market integrity, set impact tolerances for each, and prove through testing that they can stay within those tolerances during a severe-but-plausible disruption.
The transition period ended 31 March 2025, so this is a live operational requirement, not a future one. Corpsoft Solutions builds the monitoring, failover, and incident detection that make this testable in practice, not just documented on paper.
Consumer Duty requires firms to evidence that their products and services deliver good outcomes for retail customers, which in practice means your data pipelines and reporting need to capture and surface the right signals, not just uptime or transaction counts. Corpsoft Solutions builds this reporting layer on top of the operational resilience controls already in place, so the two efforts reinforce each other instead of running separately.
Software development partner. Consultancies identify your important business services and set your impact tolerances. We build the systems, monitoring, and failover that keep those services inside tolerance, and the documentation that proves it during a review. Most clients come to us after a consultancy's gap report, when the question becomes who actually builds what the report describes.
Ready to discuss your project with us?Not sure where to start?
Drop us a line about your project or challenge — we'll take it from there.
 Typical response time1 hour on business days