MSP Compliant Software Development
Turn compliance into a service you can scale.
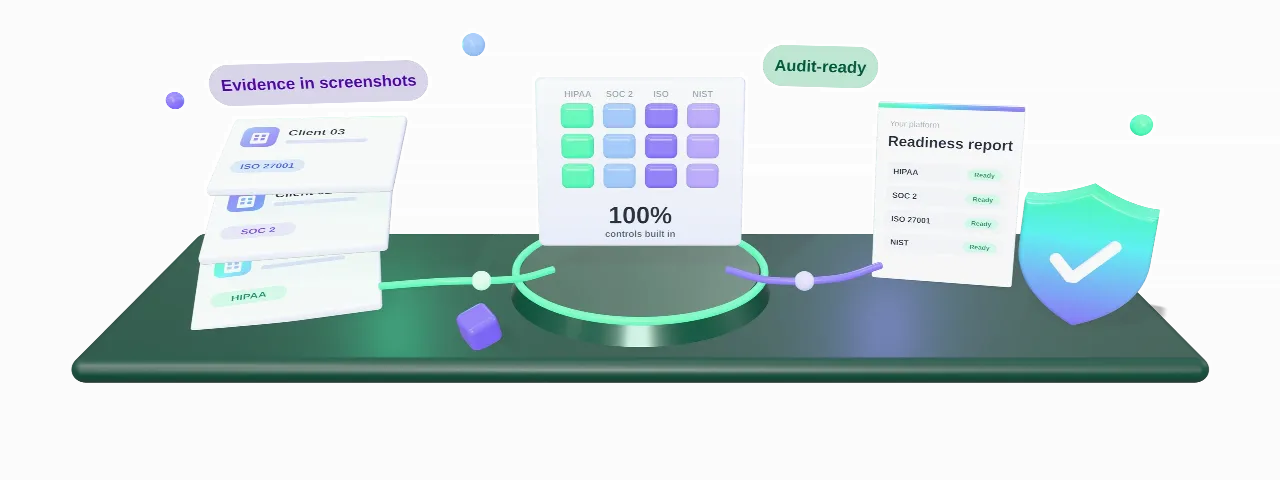
Your platform gets multi-tenant compliance tracking, automated evidence collection and audit-ready reports for SOC 2, HIPAA, CMMC and NIST, across every client environment you manage.
What Is MSP Compliance?
MSP compliance means meeting the security requirements of every client you manage, from HIPAA and SOC 2 to ISO 27001 and NIST. With dozens of clients on different frameworks, evidence ends up in spreadsheets and screenshots, and every audit turns into a scramble.
Built-in compliance tooling fixes that in four ways:
One view across all clients
Every client’s control status in one dashboard, with each tenant’s data kept separate.
Evidence collected automatically
Logs, configs and access reviews flow in from your RMM and PSA tools, ready for the auditor.
Map once, reuse everywhere
One control covers overlapping requirements in HIPAA, SOC 2, ISO 27001 and NIST.
Compliance as a service line
Audit-ready reports for each client turn compliance work into a recurring offering.
Benefits of a Compliance-First Approach for MSPs
Prevent service shutdowns or fines from regulatory breaches
Impress enterprise clients and pass vendor onboarding faster
Increase operational maturity and reduce risk exposure
Scale your MSP workforce solutions with structured security
Gain peace of mind with 24/7 compliance visibility
Ready to Build a Compliant MSP Framework?
Assess Your Current MSP Compliance LevelOur Process for MSP Compliance Development
- 01
Compliance Gap Analysis & MSP Risk Assessment
We assess your current operations, policies, and service architecture to identify vulnerabilities across MSP regulations.
- 02
Policy & Procedure Design
We draft or refine your MSP compliance policy, aligning it with HIPAA, SOC 2, ISO, or other relevant standards.
- 03
Secure MSP Architecture Development
Our team builds and updates your service workflows and platforms to include built-in compliance, ideal for MSP billing software or MSP workforce solutions.
- 04
Testing, Validation & Controls
We conduct internal tests, simulate MSP audit scenarios, and implement controls to ensure ongoing compliance.
- 05
Audit Documentation & Certification Support
We provide comprehensive documentation for audits, including data maps, vendor lists, incident logs, access reports, and policy records.
- 06
Continuous Compliance Monitoring
We help you implement automated MSP reporting tools and tracking systems to stay compliant at scale, even as regulations evolve.
MSP Compliant Software from Day One
Bring your current setup. In one call, we’ll review your platform against your clients’ frameworks. You’ll leave with: ✓ Control map for each client framework ✓ Prioritized list of gaps ✓ Architecture recommendations for multi-tenant setup
Talk to AndriiMSP Compliant Software from Day One
Bring your current setup. In one call, we’ll review your platform against your clients’ frameworks. You’ll leave with: ✓ Control map for each client framework ✓ Prioritized list of gaps ✓ Architecture recommendations for multi-tenant setup
Talk to Andrii
Andrii Svyrydov
Founder and CEO of Corpsoft Solutions
Questions clients ask before we start
FAQ
HIPAA (for MSP in healthcare), SOC 2, ISO 27001, and NIST frameworks are most commonly applied depending on the client industry and data types.
By embedding MSP compliance policy controls into onboarding, reporting, vendor selection, and client service workflows using compliance-first platforms and automation tools.
Best practices recommend conducting quarterly internal audits and annual external reviews to maintain strong MSP audit readiness and avoid surprises.
Ready to discuss your project with us?Not sure where to start?
Drop us a line about your project or challenge — we'll take it from there.
 Typical response time1 hour on business days