EU NIS2 Compliant Software Development
NIS2-ready systems, engineered into your product.
Your systems get the Article 21 security measures NIS2 requires: access management, incident detection, supply chain security and audit-ready documentation, built alongside your product roadmap.
 AWS Partner, Select Tier
 NIS2 · GDPR · ISO 27001 · SOC 2
 Free 7-day gap assessment
 EU data residency on AWS
NIS2 non-compliance is a leadership problem, not an IT backlog item.
Article 20 of the NIS2 Directive holds management bodies personally liable for cybersecurity failures. For essential entities, the fine ceiling is €10,000,000 or 2% of global annual turnover — whichever is higher. For important entities: €7,000,000 or 1.4%. The enforcement deadline passed in October 2024. Most EU companies in scope have a gap between what their systems do and what Article 21 requires.
A report, no controls
"Our security consultant delivered a 60-page report. Nobody offered to implement a single control."
No technical starting point
"We know NIS2 applies to us. We have no idea where to start technically."
No time to stop
"We cannot stop product development for six months to rebuild our security architecture."
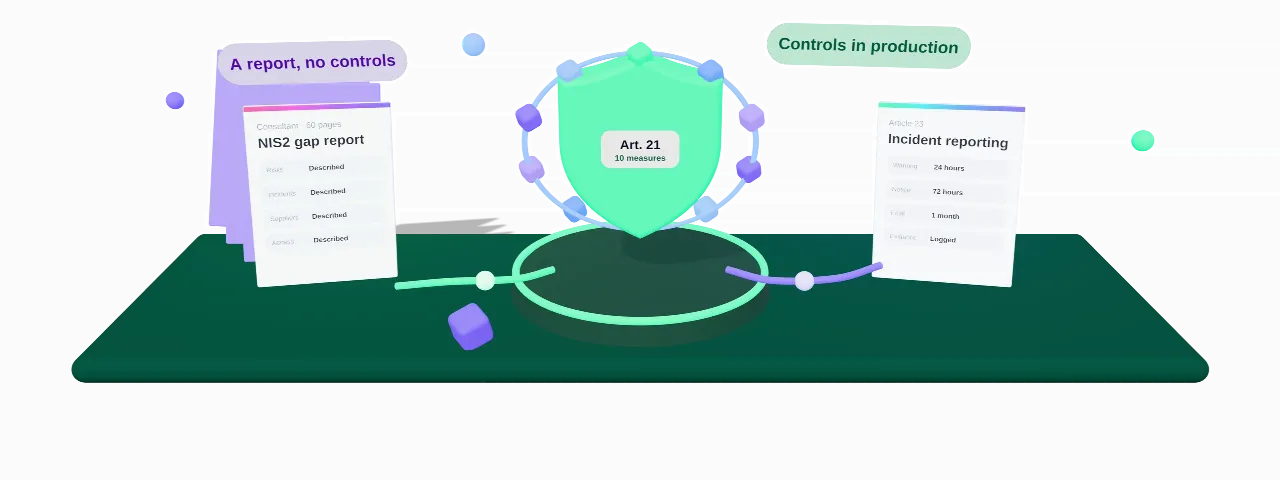
NIS2 compliance built into your systems — not added on top.
Corpsoft Solutions implements Article 21 technical requirements directly in your architecture. Access control, encryption, incident detection pipelines, supply chain risk controls, vulnerability management, and audit logging — working in production, not described in a roadmap. Every engagement closes with a documentation package that demonstrates compliance to your national competent authority.
NIS2 Readiness Assessment
A 7-day technical audit of your systems against all Article 21 requirements. Delivers a prioritized gap report with a remediation roadmap — ranked by regulatory risk and implementation complexity.
Technical Remediation and Architecture Hardening
Engineering the security controls Article 21 requires into your production systems. Access controls, encryption, network segmentation, secure configurations, and vulnerability handling — implemented, not documented.
Incident Response System Build
Detection-to-notification pipeline built into your architecture: automated alerting, 24-hour early warning capability, 72-hour incident notification workflow, and 30-day final report process — aligned with NIS2 Article 23 reporting obligations.
Supply Chain Security Program
Third-party risk assessment framework, vendor security evaluation criteria, and contractual security requirements for supplier relationships — aligned with Article 21(3) supply chain obligations.
NIS2 Documentation Package
Policy documents, procedures, incident response plans, and audit evidence artifacts. Written by the engineers who built the controls — not by consultants who reviewed them.
Continuous Vulnerability Management
Recurring automated scanning, risk prioritization, and remediation — starting at $200/month. Maintains NIS2 compliance status after implementation and prevents security debt from accumulating.
What working with Corpsoft Solutions looks like in numbers
7 days
To a gap report
From engagement start to a complete gap report with a prioritized remediation roadmap.
100%
Article 21 measures addressed
All ten security measure categories, covered in every full remediation engagement.
24 h.
To an early warning
NIS2’s deadline for alerting authorities to a significant incident. Detection and logging are built so your team can meet it.
5.0
Rating on Clutch
Across 20+ verified client reviews in healthcare, AI and enterprise SaaS.
Not sure where your NIS2 gaps are? We will tell you in 7 days.
Corpsoft Solutions audits your architecture against every Article 21 requirement and delivers a prioritized remediation plan — before a supervisory authority audits it for you.
Book a scoping callHow NIS2 compliance implementation works
- 01
Entity classification
Establish whether your organization qualifies as an Essential or Important entity, which Annex applies, and your specific obligations under the applicable national transposition of NIS2.
- 02
Technical gap assessment
Seven-day audit of your architecture, access controls, network configuration, incident response capability, encryption posture, and supply chain relationships — benchmarked against all Article 21 requirements.
- 03
Remediation roadmap
Prioritized implementation plan that separates critical regulatory gaps from lower-priority improvements, sequenced so engineering continues in parallel with compliance work.
- 04
Technical implementation
Corpsoft Solutions engineers the required controls into your production systems: access control, encryption, incident detection pipelines, vulnerability management, network hardening, and business continuity mechanisms.
- 05
Documentation and evidence package
Policies, procedures, configuration records, incident response plans, and audit artifacts — prepared alongside implementation and ready for submission to competent authorities.
After NIS2 implementation
Corpsoft Solutions delivers working technical controls. After implementation, your systems meet Article 21 requirements in production — and your team can demonstrate that to any national competent authority with the documentation we produce alongside the engineering work.
Article 21 controls in production
All ten NIS2 security measure categories implemented and operational — not in a roadmap, not in a policy document, but in your running systems.
Article 23 incident reporting ready
Automated detection pipeline delivers the 24-hour early warning, 72-hour formal notification, and 30-day final report capability NIS2 Article 23 requires.
Management liability addressed
Documentation demonstrating that management bodies fulfilled Article 20 oversight obligations — executive accountability is evidenced, not assumed.
Supply chain risk managed
Third-party vendor security assessments complete, security requirements embedded in supplier contracts, and ongoing risk monitoring active per Article 21(3).
Continuous vulnerability management
Recurring scanning, prioritization, and remediation — compliance status maintained after go-live, not just at the moment of assessment.
Audit-ready evidence package
Policies, logs, configuration records, and incident history organized for competent authority review — available the day an audit is requested.
Trusted by growing companies, past the MVP stage
Check out what they have to say about working with us.
“We could mention their technical expertise and wonderful work, but communication is their most impressive trait.”
The client has saved $200,000 and gained an incalculable amount of new business thanks to the platform’s efficiency and professional look. Corpsoft.io has delivered outstanding work, but they’ve excelled overall in project management. They use SCRUM sprints and Jira and are responsive partners.
Check out what they have to say about working with us.
“We could mention their technical expertise and wonderful work, but communication is their most impressive trait.”
The client has saved $200,000 and gained an incalculable amount of new business thanks to the platform’s efficiency and professional look. Corpsoft.io has delivered outstanding work, but they’ve excelled overall in project management. They use SCRUM sprints and Jira and are responsive partners.
NIS2 compliance in practice
See how one startup shipped HIPAA-compliant AI diagnostics 3 weeks ahead of schedule. And another one scaled to 10,000+ patients while meeting HIPAA and SOC 2 requirements.
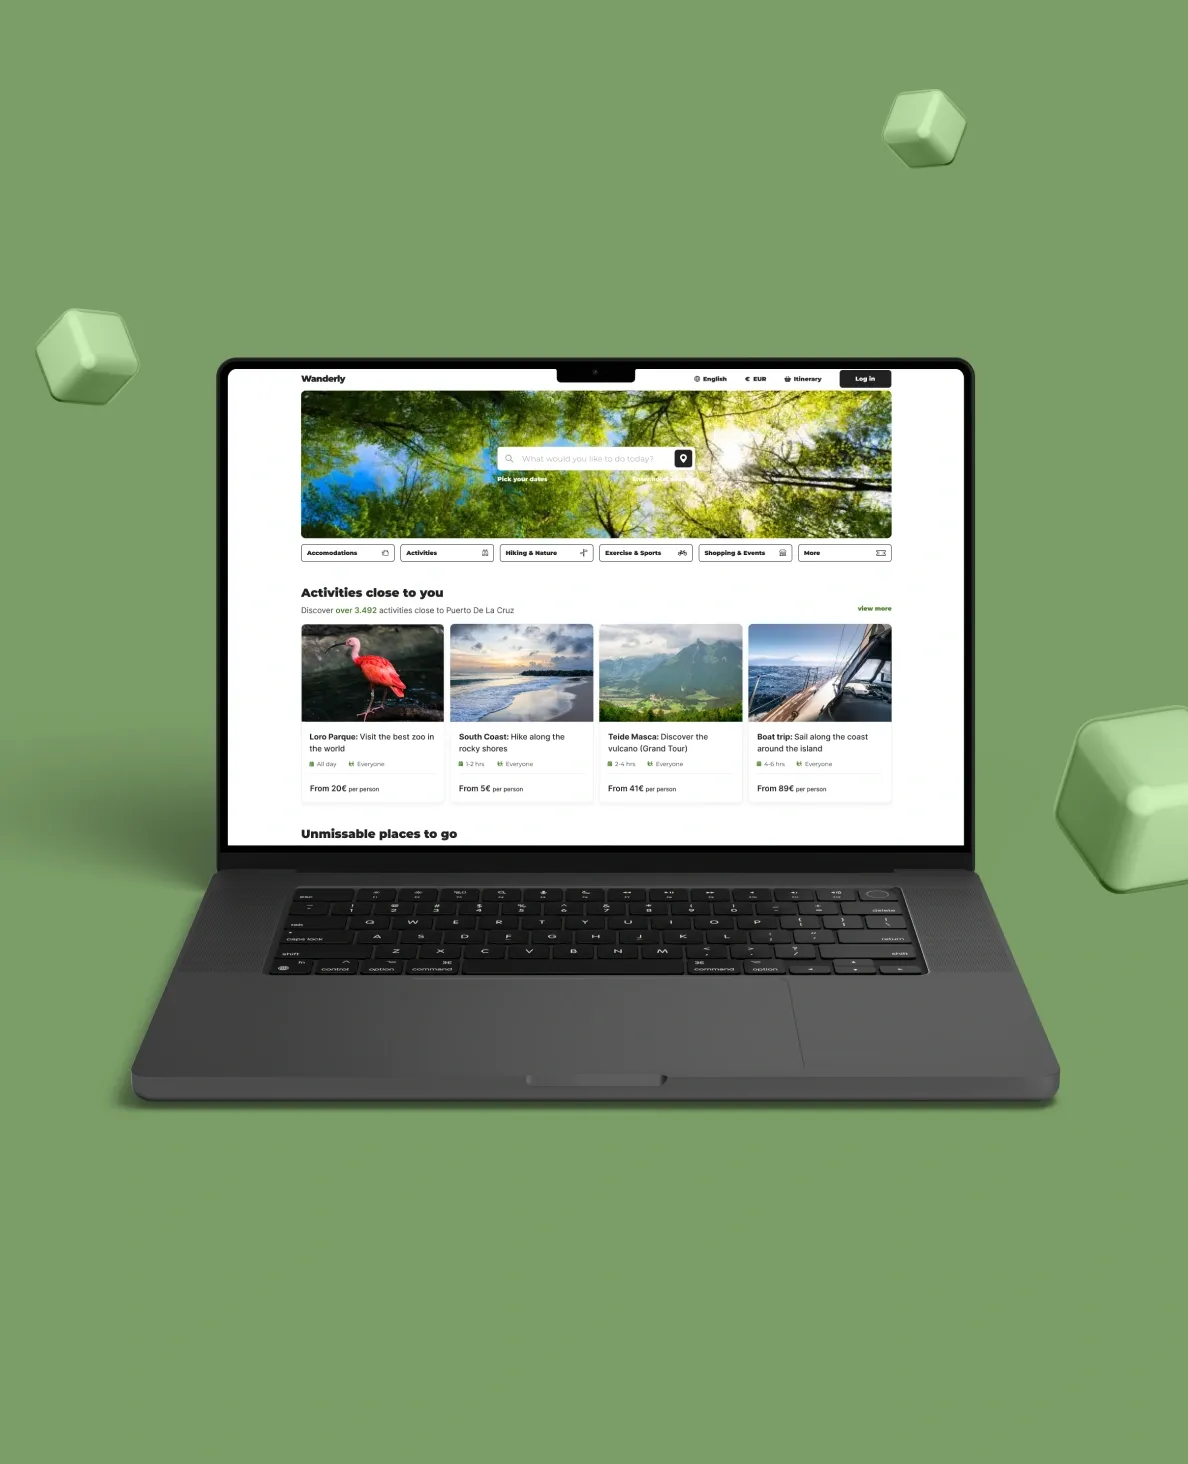
Travel booking platform raised booking conversion 30% with a live activity map
Activities scattered across several booking sites
Hard to find nearby events in real time
Syncing hotel data and third-party activities
Protecting traveler and payment data under GDPR
Single catalog with filters for location and availability
Interactive map with live events and route building
API integrations with hotel databases and aggregators
Encryption and access controls aligned with GDPR
- 30% higher booking conversion with map-based search
- First release live in 3 months
- Scalable architecture ready for new cities and languages
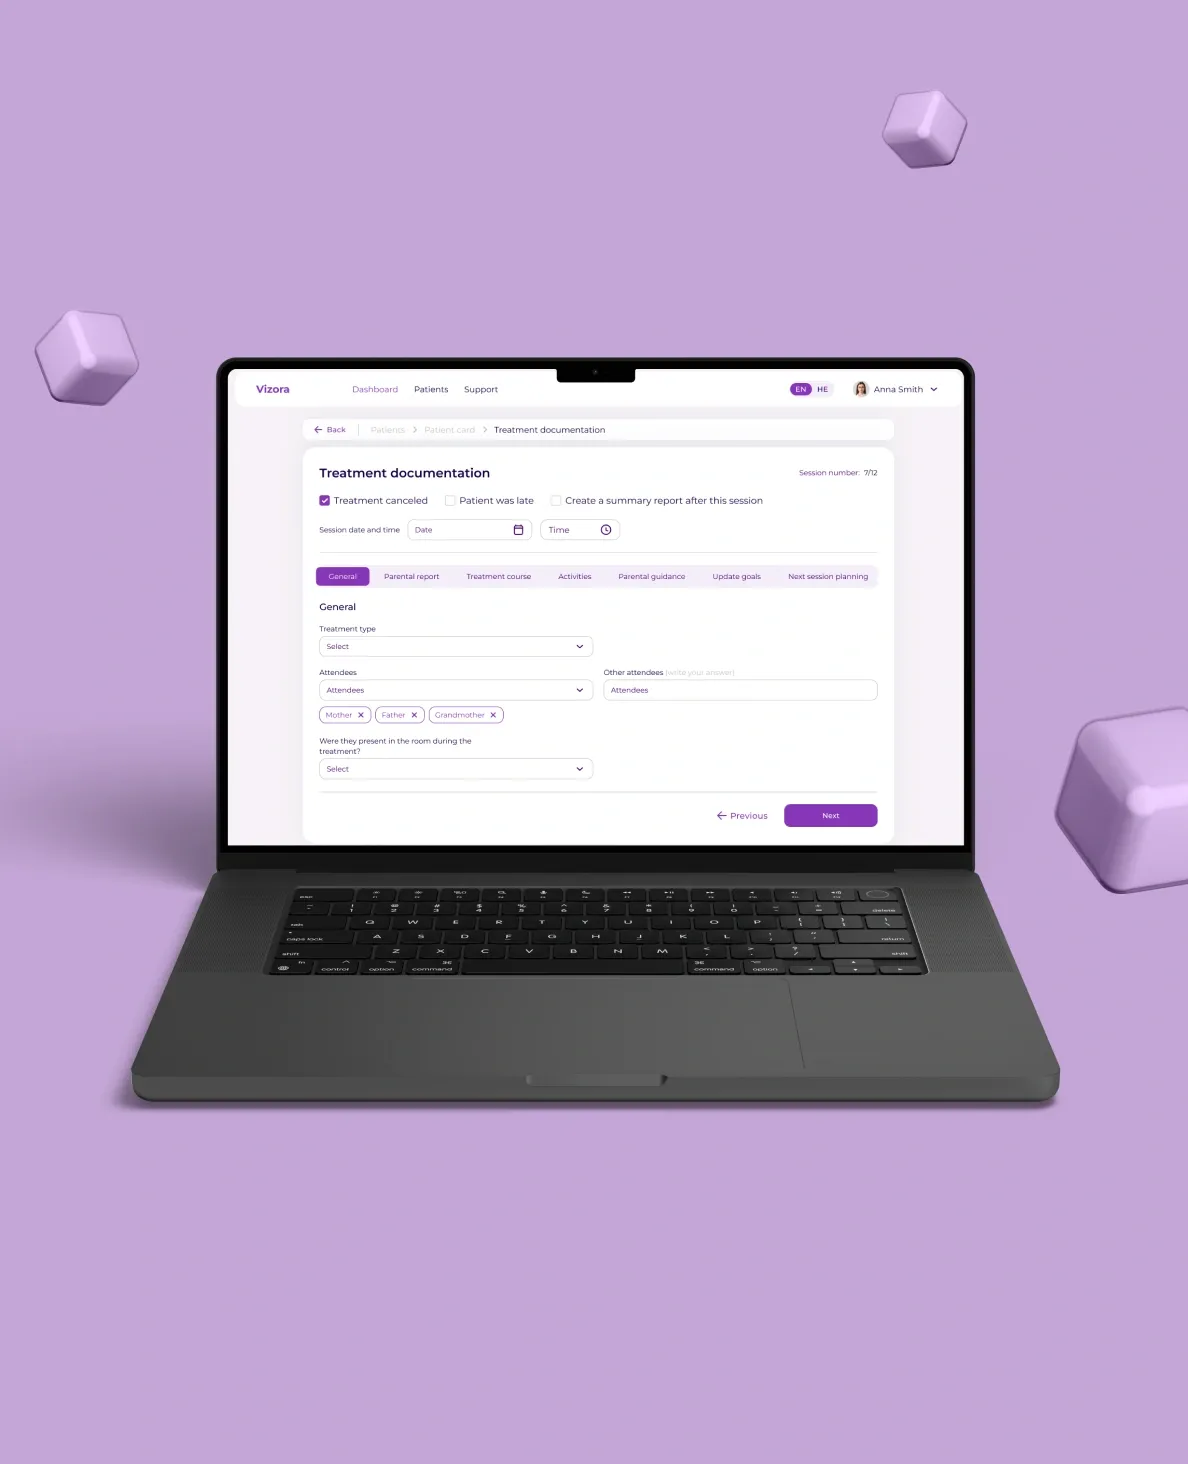
A Revolutionizing Platform For Pediatric with AI-Powered Workflow Optimization
Paperwork and slow access to patient data
Protecting patient data processed by AI
AI summaries and two-click access to patient records
Encrypted PHI storage with role-based access controls
- Treatment summary reports cut from 45 to 5 minutes
- Fully digital patient registration and records
- More time for patient care and higher daily capacity
- Real-time dashboard tracking time saved
Find your NIS2 gaps before your regulator does.
Your systems get a 7-day technical gap assessment against Article 21 requirements, with a remediation roadmap prioritized by risk.
Book a call with AndriiFind your NIS2 gaps before your regulator does.
Your systems get a 7-day technical gap assessment against Article 21 requirements, with a remediation roadmap prioritized by risk.
Book a call with Andrii
Andrii Svyrydov
Founder & CEO of Corpsoft Solutions · ex-Head of Tech at a software company with 1,500+ delivered projects
Questions clients ask before we start
NIS2 covers organizations in 18 sectors across the EU and EEA. Coverage applies to medium-sized enterprises (50+ employees or €10M+ annual revenue) operating in sectors listed in Annex I or Annex II. Covered sectors include energy, transport, health, banking, financial market infrastructure, digital infrastructure, ICT service management (B2B), food production, manufacturing of medical devices and electronics, digital providers, and research organizations, among others. If you are uncertain whether your organization falls in scope, entity classification is the first deliverable of the Corpsoft Solutions gap assessment.
The gap assessment is completed in 7 days. Full technical remediation typically takes 6–16 weeks, depending on the number of critical gaps, the complexity of the existing architecture, and the security controls already in place. Corpsoft Solutions provides a specific timeline after the gap assessment, with milestones tied to regulatory risk — the highest-exposure gaps are addressed first.
For essential entities: up to €10,000,000 or 2% of total global annual turnover, whichever is higher. For important entities: up to €7,000,000 or 1.4% of global annual turnover. Beyond financial penalties, Article 34 authorizes national competent authorities to issue temporary bans on individuals exercising management functions, publicly disclose the organization and the nature of the violation, and suspend certifications or authorizations relevant to the services the entity provides.
Yes. Corpsoft Solutions sequences remediation to run in parallel with your product roadmap. The gap assessment identifies which controls can be implemented at the infrastructure and configuration level without touching core product code — in most cases, the majority of Article 21 work falls into that category. Where application-layer changes are required, Corpsoft Solutions coordinates with your engineering team to minimize roadmap impact.
Ready to discuss your project with us?Not sure where to start?
Drop us a line about your project or challenge — we'll take it from there.
 Typical response time1 hour on business days